Cyber Kill Chain
Lockheed Martin – Cyber Kill Chain
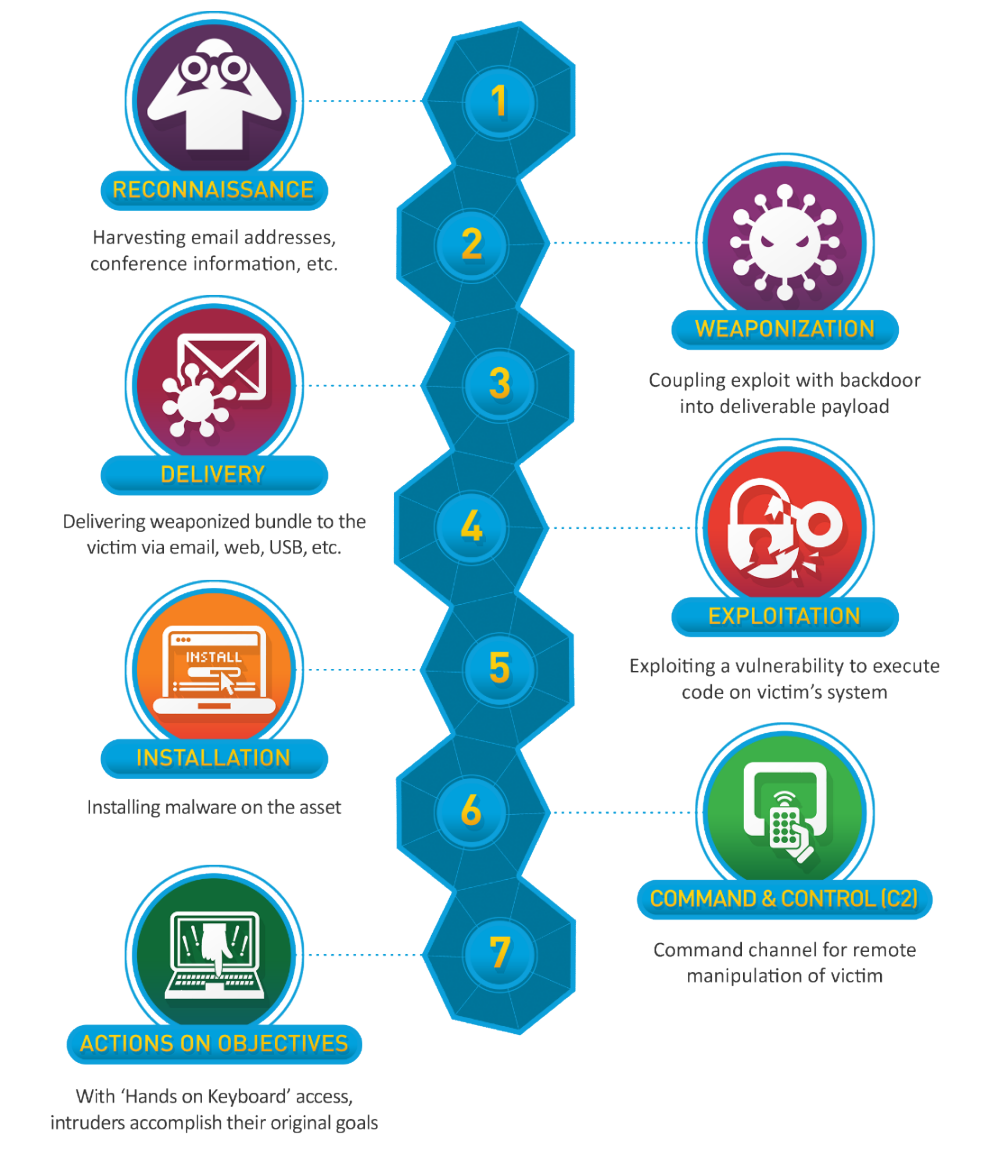
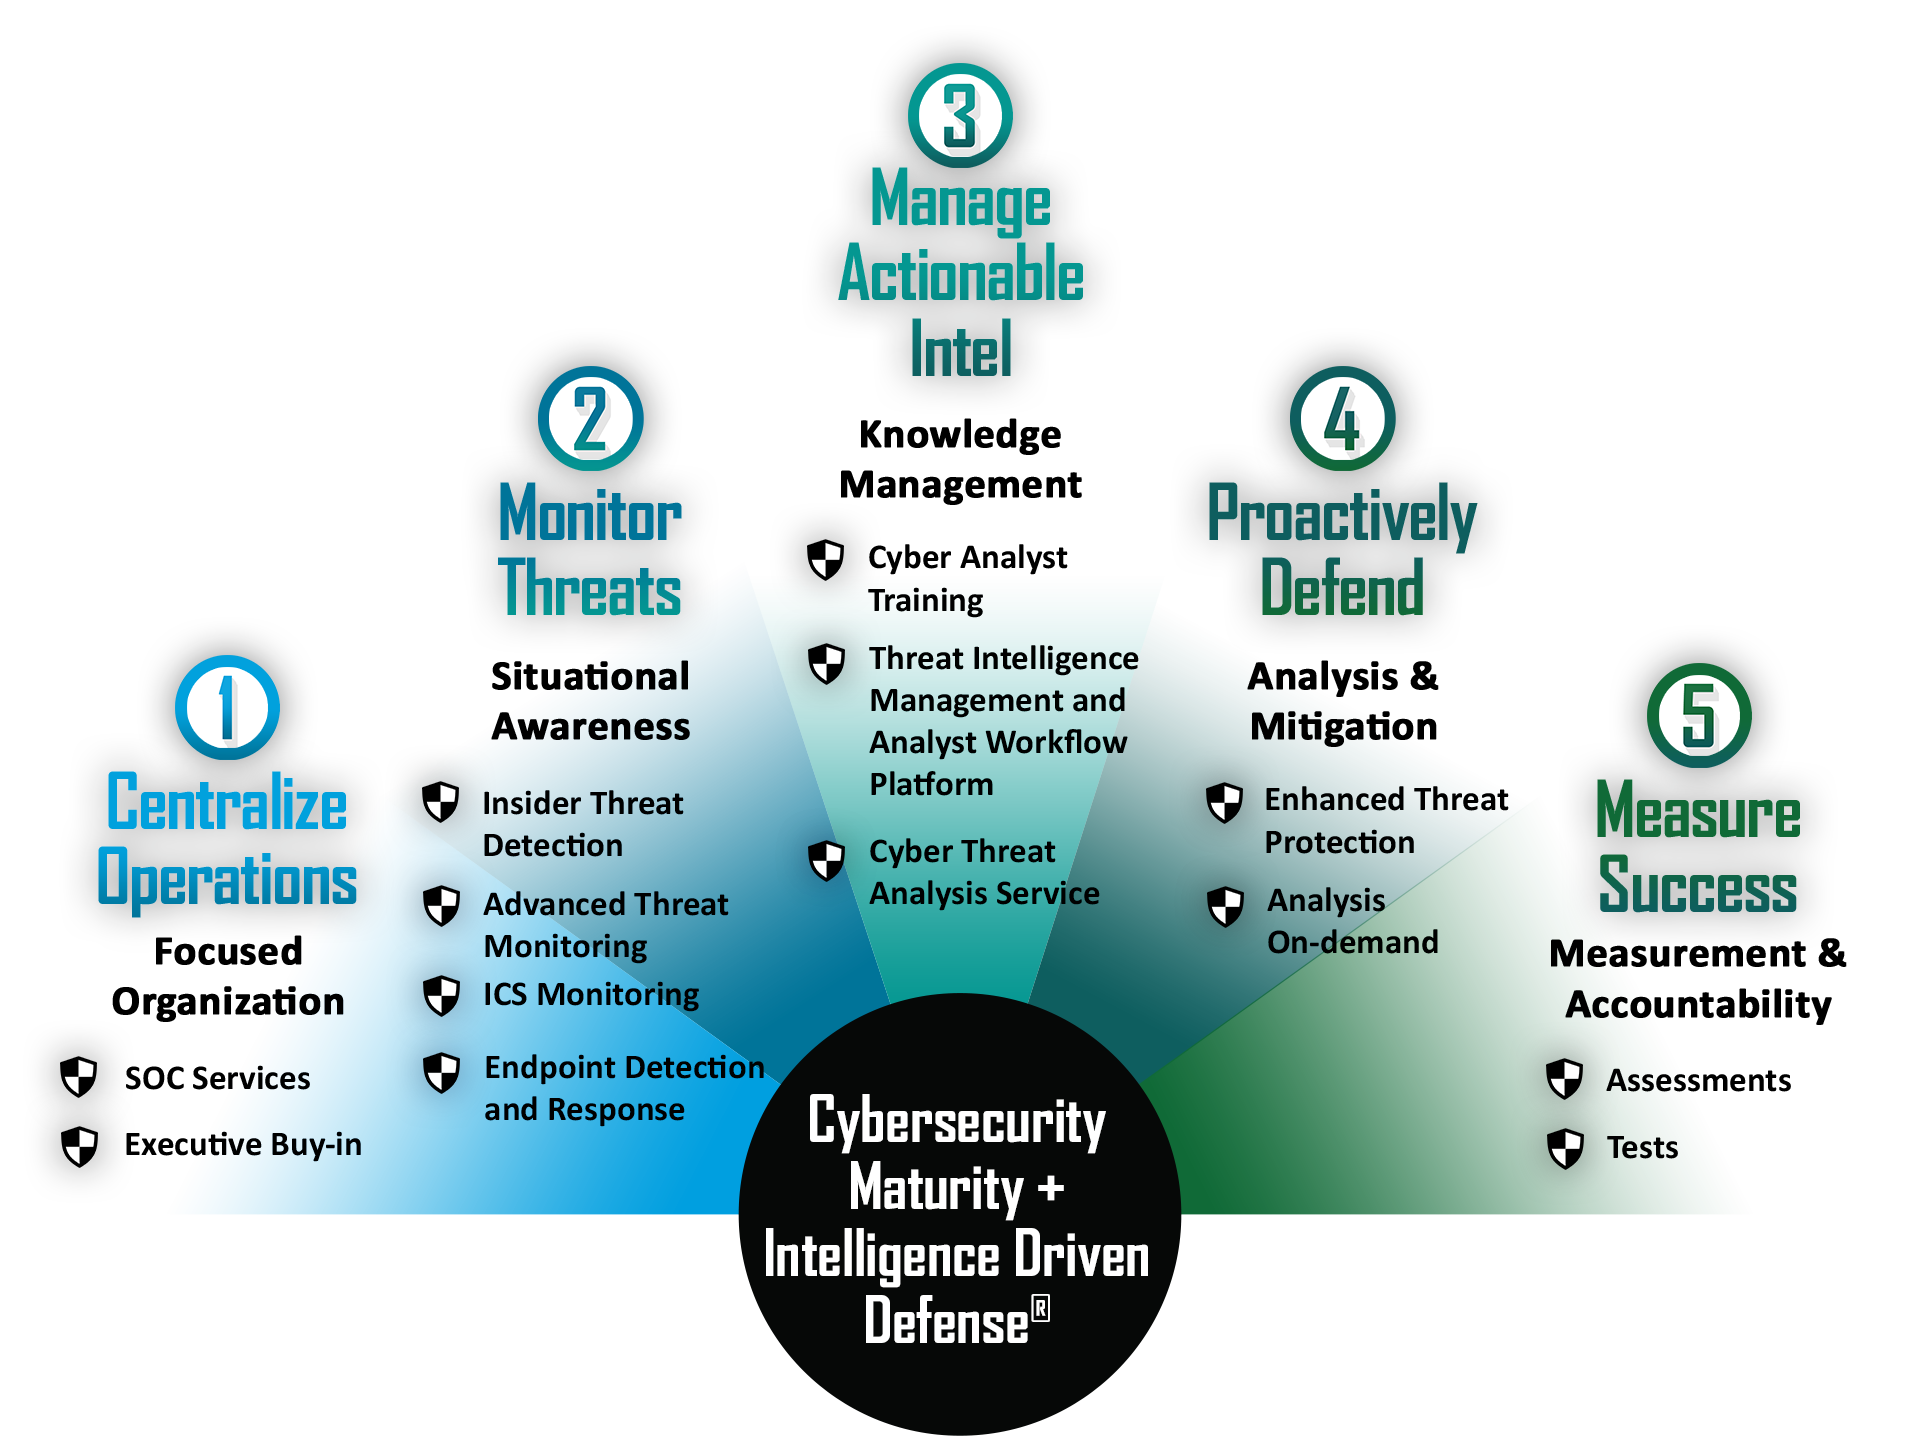
Developed by Lockheed Martin, the Cyber Kill Chain® framework is part of the Intelligence Driven Defense® model for identification and prevention of cyber intrusions activity. The model identifies what the adversaries must complete in order to achieve their objective.
The seven steps of the Cyber Kill Chain® enhance visibility into an attack and enrich an analyst’s understanding of an adversary’s tactics, techniques and procedures.
FireEye Mandiant Attacker Lifecycle


MITRE ATT&CK
- Initial Access
- Execution
- Persistence
- Privilege Escalation
- Defence Evasion
- Credential Access
- Discovery
- Lateral Movement
- Collection
- Command and Control
- Exfiltration
- Impact
Pyramid of Pain

http://detect-respond.blogspot.com/2013/03/the-pyramid-of-pain.html
CIA Triad


- Level 1: Initiate: This level is for people new to the information security industry, folks who are rapidly building their skills from the ground up.
- Level 2: Padawan: These folks have achieved some really solid capabilities, and represent the largest player community in NetWars, as they work to build their skills even further to differentiate themselves from the pack.
- Level 3: Guardian: People at this level have achieved something quite significant: they’ve exceeded the capability of the average info sec person, and proudly continue to grow to the next level.
- Level 4: Knight: Some people say that there’s a phrase for NetWars participants who achieve this level: “Hire ’em.” That’s due to their really awesome skills in solving even the trickiest infosec challenges.
- Level 5: Master: When you reach this level, we figure that you’re so good, there’s nothing we can throw at you to challenge you… except other people like you. Just as steel sharpens steel, in Level 5, master infosec gurus battle against each other in a castle-vs-castle face-off.

Funnel of Fidelity

https://posts.specterops.io/introducing-the-funnel-of-fidelity-b1bb59b04036
https://posts.specterops.io/detection-spectrum-198a0bfb9302
lo

NIST
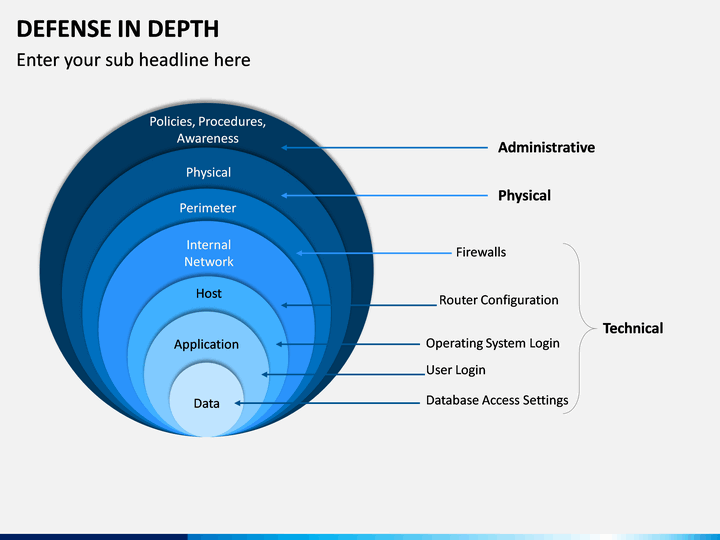
Defence In-depth


040813_northrop_grumman_response_part2
False Positives / False-negatives

Mean-Time to Detect Mean-Time to Recover (BIA/RPO/RTO.)

Do More with less vs Skills shortage vs increased skills vs burn-out

Cyber Threat Framework
- https://www.dni.gov/index.php/cyber-threat-framework
- https://csrc.nist.gov/CSRC/media/Projects/cyber-supply-chain-risk-management/documents/SSCA/Fall_2018/WedPM2.2-STARCAR%20SCRM%20FINAL%20508.pdf
Examples Mapped to CVEs and MITRE
- https://github.com/BankSecurity/Red_Team
- https://www.fireeye.com/blog/threat-research/2018/10/apt38-details-on-new-north-korean-regime-backed-threat-group.html
- https://www.fireeye.com/blog/threat-research/2019/03/apt40-examining-a-china-nexus-espionage-actor.html
- https://www.fireeye.com/blog/threat-research/2016/08/wmi_vs_wmi_monitor.html
Reference
- Applying Cyber Kill Chain® Methodology to Network Defense
- Seven Ways to Apply the Cyber Kill Chain® with a Threat Intelligence Platform
- Achieving Cyber Security by Designing for Intelligence Driven Defense®
- A Threat-Driven Approach to Cyber Security
- Intelligence-Driven Computer Network Defense Informed by Analysis of Adversary Campaigns and Intrusion Kill Chains
- https://www.sans.org/cyber-security-summit/archives/file/summit-archive-1543954745.pdf