
Here is my brain dump of Cyber Security interview questions from the past, after every interview, I wrote down the questions and made up my own for preparation. I hope this helps someone get a job and take care of your family.
Advise for Hiring managers
You should allow the candidate to ask you 3 technical questions in return, too many times, I’ve had technical questions from interviewers who got the answer incorrect. or blast through a list questions. Someone times hiring people get these answers wrong or could not even pass their own interviews.
I would ask experience based question, for a Solution Architect for a Solutions Integrator, give me a example of how you wrote a SOW and the process you went about doing that and pick apart that answer or Explain how you would design X solution?
Take One Day, One Step at a Time.
Some advice; I was recently out of work and going to multiple interviews for Email Security, to Micro segmentation to Identify Architect, If you are in this situation, it is very difficult, as you are doing multiple interviews per day and may need to do multiple technical interviews and even presentations and even proposals and even write code and build environments inside cloud. This is not an ideal situation, getting a job is very difficult. The best way is to apply for a single job and really research exactly the requirements and prepare, which takes allot of investment in time and of course, there is always luck of the draw. So take One day and One step at a time.
Treat technical cybersecurity interviews as an opportunity to demonstrate curiosity, capability, and ongoing development. Show what you build at home, how you learn, and how you contribute to the community. Move beyond a basic home lab and develop projects that reflect practical experience, such as DFIR work, AI security research, community engagement, or technical content creation.
Use platforms like blogs, communities, podcasts, and YouTube to share insights and sharpen your communication skills. Ensure this body of work is visible and easy for hiring managers to understand, so it supports your applications rather than getting overlooked.
Stay focused on solving complex problems, continuous learning, and demonstrating the energy you will bring to a high-performing security team. If an organisation values professionals who actively practise technical cybersecurity and AI, remain open to discussions and new roles.
I found this very useful for Webcam interviews;
Cyber Security Interview Questions
| What is the ‘Shadow file’ and location | The shadow file is probably one of the most important files on your linux system, and that’s because it stores the actual encrypted passwords for everything on your system. The shadow file is located at /etc/shadow, and is only accessible to the root user. https://linuxhint.com/shadow-password-file-linux/ |
| Explain ASEP keys | Auto-Start Extensibility Points (ASEPs is specific areas within in the Windows Operating System, that can be used by Malware to maintain persistence such as the Run key inside the registry; KEY_CURRENT_USERSoftwareMicrosoftWindowsCurrentVersionRun HKEY_CURRENT_USERSoftwareMicrosoftWindowsCurrentVersionRunOnce https://resources.infosecinstitute.com/topic/common-malware-persistence-mechanisms/ |
| What is the LSASS Driver | The Windows security subsystem is a set of components that manage and enforce the security policy for a computer or domain. The Local Security Authority (LSA) is the main component responsible for local security policy and user authentication. The LSA includes multiple dynamic link libraries (DLLs) associated with various other security functions, all of which run in the context of the LSA Subsystem Service (LSASS) lsass.exe process. https://www.ired.team/offensive-security/credential-access-and-credential-dumping/dump-credentials-from-lsass-process-without-mimikatz https://attack.mitre.org/techniques/T1547/008/ https://medium.com/@markmotig/some-ways-to-dump-lsass-exe-c4a75fdc49bf |
| What is the Registry Hive | The registry is a hierarchical database that contains data that is critical for the operation of Windows and the applications and services that run on Windows. The data is structured in a tree format. Each node in the tree is called a key. Each key can contain both subkeys and data entries called values. Sometimes, the presence of a key is all the data that an application requires; other times, an application opens a key and uses the values associated with the key. A key can have any number of values, and the values can be in any form. For more information, see Registry Value Types and Registry Element Size Limits. https://learn.microsoft.com/en-us/windows/win32/sysinfo/structure-of-the-registry?source=recommendations HKEY_CURRENT_CONFIG System, System.alt, System.log, System.sav HKEY_CURRENT_USER Ntuser.dat, Ntuser.dat.log HKEY_LOCAL_MACHINE\SAM Sam, Sam.log, Sam.sav HKEY_LOCAL_MACHINE\Security Security, Security.log, Security.sav HKEY_LOCAL_MACHINE\Software Software, Software.log, Software.sav HKEY_LOCAL_MACHINE\System System, System.alt, System.log, System.sav HKEY_USERS\.DEFAULT Default, Default.log, Default.sav |
| Explain AAA? | AAA stands for authentication, authorization, and accounting. AAA is a framework for intelligently controlling access to computer resources, enforcing policies, auditing usage, and providing the information necessary to bill for services. These processes working in concert are important for effective network management and security. Authentication Authentication provides a method of identifying a user, typically by having the user enter a valid username and password before access to the network is granted. Authentication is based on each user having a unique set of login credentials for gaining network access. The AAA server compares a user’s authentication credentials with other user credentials stored in a database; in this case, that database is Active Directory. If the user’s login credentials match, the user is granted access to the network. If the credentials don’t match, authentication fails and network access is denied. Authorization Following authentication, a user must gain authorization for doing certain tasks. After logging in to a system, for instance, the user may try to issue commands. The authorization process determines whether the user has the authority to issue such commands. Simply put, authorization is the process of enforcing policies—determining what types or qualities of activities, resources, or services a user is permitted. Usually authorization occurs within the context of authentication. After you have authenticated a user, they may be authorized for different types of access or activity. As it relates to network authentication via RADIUS and 802.1x, authorization can be used to determine what VLAN, Access Control List (ACL), or user role that the user belongs to. Accounting The final piece in the AAA framework is accounting, which monitors the resources a user consumes during network access. This can include the amount of system time or the amount of data sent and received during a session. Accounting is carried out by logging session statistics and usage information. It is used for authorization control, billing, trend analysis, resource utilization, and planning for the data capacity required for business operations. ClearPass Policy Manager functions as the accounting server and receives accounting information about the user from the Network Access Server (NAS). The NAS must be configured to use ClearPass Policy Manager as an accounting server, and it is up to the NAS to provide accurate accounting information to ClearPass Policy Manager. |
| What is a Three-Way Handshake? | The TCP handshake TCP uses a three-way handshake to establish a reliable connection. The connection is full duplex, and both sides synchronize (SYN) and acknowledge (ACK) each other. The exchange of these four flags is performed in three steps: SYN, SYN-ACK, ACK.  https://www.techopedia.com/definition/10339/three-way-handshake https://www.sciencedirect.com/topics/computer-science/three-way-handshake https://learn.microsoft.com/en-GB/troubleshoot/windows-server/networking/three-way-handshake-via-tcpip |
| What port uses SSH? What port uses DNS? | Port 22 Port 53, DNS operates a Layer 7. |
| What is Risk and Risk Management? | Risk can be defined as the ‘effect of uncertainty on objectives’. Risk is important as it assists organisations in setting strategy, achieving objectives and making informed decisions. Taking risks is fundamental to organisations Cybersecurity risk management is a strategic approach to prioritizing threats. Organizations implement cybersecurity risk management in order to ensure the most critical threats are handled in a timely manner. This approach helps identify, analyze, evaluate, and address threats based on the potential impact each threat poses. https://www.imperva.com/learn/data-security/cybersecurity-risk-management/ A mentee reached out for CISSP help. Sharing my notes on the high level processes to measure Organizational Risk and Quantify Impact. Effective Risk Management enables businesses to proactively prioritize risk treatments and maximize returns on security investments. Scale is a challenge. How to Measure Risk: 1. Determine Asset Values: The value of an asset is more than the out-of-pocket dollars required to obtain the assets. • Determining Asset values is a foundational part of the overall risk vs. impact analysis process that helps an organization understand the possible financial impact on the enterprise concerning a specific threat. • Qualitative – subjective values based on assets worth to the organization • Quantitative- values based on assets cost 2. Measure: • The initial and ongoing cost to the enterprise for purchasing/licensing/ developing and supporting the environment or information asset • An assets value to the enterprise production operations R&D in core business viability • An asset’s value established on the external marketplace and the estimated value of the intellectual property such as trade secrets, patents, copyright • An asset’s value to an adversary • Cost to replace if the asset is lost • Operational costs incurred if unavailable • Liability issues if the asset is compromised 3. Perform Security Risk Analysis Steps: • Assign a value to information and assets • Estimate potential loss of risk • Perform threat analysis • Remedial measures to counteract each risk • Reduce, Assign, Transfer, or Accept the risk 4. Determine Financial Impact & Investment Threshold: • Impact analysis is concerned with calculating the potential financial impact of threats to various assets. A. Determine exposure factor: Single loss expectancy * asset value = exposure The exposure is the percent of an asset loss caused by an identified threat. E.G.- If a hurricane hits my business office and generates 50% destruction, then the exposure factor is 50% B. Determine Single Loss Expectancy (SLE): Asset Value * Exposure factor = SLE For the business office example, the SLE would be 1billion x .05 = 500 million C. Determine Annualized Rate of Occurrence: The Annualized rate of occurrence is the possibility of a specific threat occurring within a year. If a hurricane season is only 20% of a year, then the annualized rate of occurrence is 20% D. Determine Annualized Loss Expectancy: To calculate the annualized loss expectancy for a company per year, multiply the SLE by the annualized rate of occurrence. Example: SLE (500 million) x annualized rate of occurrence (.20) = 100 million ALE 5. Business Insight for Risk Impact & Mitigation Cost Threshold * ALE enables cost/benefit analysis when choosing mitigating actions to reduce potential loss. *In the example, spending more than $100M on annual risk mitigation would be a waste of $ |
| What is risk vulnerability and threat? | https://www.splunk.com/en_us/blog/learn/vulnerability-vs-threat-vs-risk.html#:~:text=Vulnerability%20vs%20threat%20vs%20risk&text=In%20short%2C%20we%20can%20see,when%20the%20threat%20does%20occur. https://www.splunk.com/en_us/blog/learn/vulnerability-vs-threat-vs-risk.html#:~:text=Vulnerability%20vs%20threat%20vs%20risk&text=In%20short%2C%20we%20can%20see,when%20the%20threat%20does%20occur. |
| What is the difference between HTTP and HTTPs | HTTP sends data over port 80 while HTTPS uses port 443. HTTP operates at application layer, while HTTPS operates at transport layer. No SSL certificates are required for HTTP; with HTTPS, it is required that you have an SSL certificate and a CA signs it. |
| What is the difference between SSL/TLS What is TLS? | Transport Layer Security (TLS) is the successor protocol to SSL. TLS is an improved version of SSL. It works in much the same way as the SSL, using encryption to protect the transfer of data and information. The two terms are often used interchangeably in the industry although SSL is still widely used. When you buy an ‘SSL’ certificate from DigiCert, you can of course use it with both SSL and TLS protocols. https://www.ssl2buy.com/wiki/ssl-vs-tls https://www.cloudflare.com/en-gb/learning/ssl/transport-layer-security-tls/ |
| What port is RDP? | 3389 |
| What port is smtp | 25 most common SMTP Ports you should know about, namely Port 25, Port 465, 587- https://netcorecloud.com/blog/25-465-587-2525-choose-the-right-smtp-port/ |
| What is the difference between UDP / TCP | What is TCP? Transmission Control Protocol (TCP) is connection-oriented, meaning once a connection has been established, data can be transmitted in two directions. TCP has built-in systems to check for errors and to guarantee data will be delivered in the order it was sent, making it the perfect protocol for transferring information like still images, data files, and web pages. But while TCP is instinctively reliable, its feedback mechanisms also result in a larger overhead, translating to greater use of the available bandwidth on your network. What is UDP? User Datagram Protocol (UDP) is a simpler, connectionless Internet protocol wherein error-checking and recovery services are not required. With UDP, there is no overhead for opening a connection, maintaining a connection, or terminating a connection; data is continuously sent to the recipient, whether or not they receive it. Although UDP isn’t ideal for sending an email, viewing a webpage, or downloading a file, it is largely preferred for real-time communications like broadcast or multitask network transmission. https://www.lifesize.com/blog/tcp-vs-udp/ |
| What is a APT? | An advanced persistent threat (APT) is a broad term used to describe an attack campaign in which an intruder, or team of intruders, establishes an illicit, long-term presence on a network in order to mine highly sensitive data. An advanced persistent threat is a stealthy threat actor, typically a nation state or state-sponsored group, which gains unauthorized access to a computer network and remains undetected for an extended period APT Groups – https://attack.mitre.org/groups/ |
| What is a IoC? | Indicator of compromise or IOC is a forensic term that refers to the evidence on a device that points out to a security breach. In this article, we discussed how IOC can be useful for your cyber security team. IPs/Domains/Hashes/Filenames/ |
| Explain the MITRE tiers? | ATT&CK Matrix for Enterprise Matrices (11 Tiers) They now have multiple Matrices that covers, Cloud, Mobile, ICS and SaaS / O365. https://attack.mitre.org/matrices/enterprise/cloud/office365/ Reconnaissance Resource Development Initial Access Execution Persistence Privilege Escalation Defense Evasion Credential Access Discovery Lateral Movement Collection Command and Control Exfiltration Impact |
| Explain Control Plane vs Data Plane (in respect to AWS? | In terms of Control Plane and Data plane, in respect to AWS, The Control Pane is the AWS management layer and the Data Plane is were the Servers, Data and Applications run. https://www.cloudflare.com/en-gb/learning/network-layer/what-is-the-control-plane/ |
| What is SSL Inspection? | https://www.zscaler.com/resources/security-terms-glossary/what-is-ssl-inspection |
| What are the 7 OSI Model layers? |  In which OSI layer is DNS? Layer 7 https://www.geeksforgeeks.org/layers-of-osi-model/?ref=leftbar-rightbar |
| What is DNS? What happens DNS when you hit www.google.com on browser Explain DNS name resolutions? The Domain Name System | (DNS) is the phonebook of the Internet. Humans access information online through domain names, like nytimes.com or espn.com. Web browsers interact through Internet Protocol (IP) addresses. DNS translates domain names to IP addresses so browsers can load Internet resources. – Each device connected to the Internet has a unique IP address which other machines use to find the device. DNS servers eliminate the need for humans to memorize IP addresses such as 192.168.1.1 (in IPv4), or more complex newer alphanumeric IP addresses such as 2400:cb00:2048:1::c629:d7a2 (in IPv6). https://www.cloudflare.com/en-gb/learning/dns/what-is-dns/   |
| What is Authoritative DNS? What is recursive DNS? | Authoritative DNS is the system that takes an address, like google.com, and provides an answer about the resources in that zone. The purpose of Recursive DNS, as we saw in step 2.1 above, is to hold information about a host for the given amount of time specified by that record’s Time To Live (TTL) Value. Recursion can happen at a number of different levels, depending on the network. Recursive DNS exists primarily to help reduce authoritative lookups, and increase the speed at which Internet users are able to access the resources they most frequently use. While ISPs provide this as a free service, there are a number of public DNS recursives that can be used as an alternative. OpenDNS and Google DNS are examples of free, public recursive servers – because they are more widely used, the recursion is aggregated globally and may result in an increase in performance when browsing the web. |
| What is SASE? | |
| What is DNS Tunnelling? | |
| How does SAML work? | SAML works by exchanging user information, such as logins, authentication state, identifiers, and other relevant attributes between the identity and service provider. As a result, it simplifies and secures the authentication process as the user only needs to log in once with a single set of authentication credentials. |
| What is a CDN? | https://www.cloudflare.com/en-gb/learning/cdn/what-is-a-cdn/ https://www.cloudflare.com/en-gb/learning/ |
| What are cookie – https://techdocs.akamai.com/home/page/manage-cookie-preferences | https://techdocs.akamai.com/home/page/manage-cookie-preferences |
| Explain DNS return code? | https://support.umbrella.com/hc/en-us/articles/232254248-Common-DNS-return-codes-for-any-DNS-service-and-Umbrella- |
| Is HTTP stateless connection? What is HTTPS/HTTP ? | https://developer.mozilla.org/en-US/docs/Web/HTTP/Overview#:~:text=HTTP%20is%20stateless%2C%20but%20not%20sessionless&text=But%20while%20the%20core%20of,the%20use%20of%20stateful%20sessions. https://www.cloudflare.com/en-gb/learning/ssl/what-is-https/ |
| Which Operating Systems would you use for different use cases/requirements? | FreeBSD – Secure / Front End Webservers + NGENIX UbuntuLTS – General Desktop OS MacOS/Windows – General User Desktop OS CentOS/RedHat – Servers AIX/System Z – Mission Critical |
| What is the AWS Shared Responsibility Model? | What is the AWS Shared Responsibility Model? |
| If you where going to develop a Prototype MVP application that needs to scale-out to millions of users quickly, how would you do it? | I would build it on top of GCP as that is IMO, the best Cloud Platform, using Serverless Code connecting to GCP Database backend and front end using either Flutter and Backend using Python, or use a existing framework such as Joomla CMS or WordPress as the basis for a MVP. I would also use QT for multi-os application and for a Machine Learning platform, use ELK stack. |
| What is a ODDA Loop? |  |
| What is a CIA Triad? | Confidentiality is roughly equivalent to privacy. Confidentiality measures are designed to prevent sensitive information from unauthorized access attempts. It is common for data to be categorized according to the amount and type of damage that could be done if it fell into the wrong hands. More or less stringent measures can then be implemented according to those categories. Integrity involves maintaining the consistency, accuracy and trustworthiness of data over its entire lifecycle. Data must not be changed in transit, and steps must be taken to ensure data cannot be altered by unauthorized people (for example, in a breach of confidentiality). Availability means information should be consistently and readily accessible for authorized parties. This involves properly maintaining hardware and technical infrastructure and systems that hold and display the information. |
| What is the Gartner SOC Visibility Triad |  |
| Explain Chain of Custody? | Chain of Custody is a term referring to the order and way physical or electronic evidence in investigations is handled. It is important to show that all evidence was handled in line with best practice procedures, by documenting all relevant details in the ‘Chain of Custody’ document. Items found to form part of an inadequate or inaccurate chain of custody document may be deemed inadmissible. |
| Explain the difference between BCP/DRP? | BCDR A business continuity plan (BCP) is a document that outlines how a business will continue operating during an unplanned disruption in service. It’s more comprehensive than a disaster recovery plan and contains contingencies for business processes, assets, human resources and business partners – every aspect of the business that might be affected. A disaster recovery plan (DRP) is a documented, structured approach that describes how an organization can quickly resume work after an unplanned incident. A DRP is an essential part of a business continuity plan (BCP). It is applied to the aspects of an organization that depend on a functioning information technology (IT) infrastructure. A DRP aims to help an organization resolve data loss and recover system functionality so that it can perform in the aftermath of an incident, even if it operates at a minimal level. |
| What is RPO/RTO? | Recovery Point Objective (RPO) describes the interval of time that might pass during a disruption before the quantity of data lost during that period exceeds the Business Continuity Plan’s maximum allowable threshold or “tolerance.” Recovery Time Objective (RTO) is the duration of time and a service level within which a business process must be restored after a disaster in order to avoid unacceptable consequences associated with a break in continuity. In other words, the RTO is the answer to the question: “How much time did it take to recover after notification of business process disruption?“ |
| What is the first things you would do for a Cyber Security Strategy? | 1. Create an Incident Response Plane and DFIR retainer for any Incidents (CSIRT). 2. Create an IT asset register? 3. Create Cyber Awareness Training? 4. Create a Cyber Strategy and Roadmap based on a BIA? 5. Establish 24/7 Detection and Response capability? 6. Ensure your BCP/DRP and Backups work. |
| What Cyber security Polcies and Frameworks are you familiar with? | Regulations / Governance / Law Australian Privacy Principles PCS-DSS (Layer 1, Layer 2, Layer 3 and Layer 4) HIPPA SOX FISMA SOX/ FISMA FedRamp Frameworks ASD Essential 8 NIST 800-53 NIST CSF CAF ISO 27001 CIS Controls SOC2 COBIT |
| Explain CVE? | CVE stands for Common Vulnerabilities and Exposures. CVE is a glossary that classifies vulnerabilities. The glossary analyzes vulnerabilities and then uses the Common Vulnerability Scoring System (CVSS) to evaluate the threat level of a vulnerability. A CVE score is often used for prioritizing the security of vulnerabilities. The CVE glossary is a project dedicated to tracking and cataloging vulnerabilities in consumer software and hardware. It is maintained by the MITRE Corporation with funding from the US Division of Homeland Security. Vulnerabilities are collected and cataloged using the Security Content Automation Protocol (SCAP). https://www.imperva.com/learn/application-security/cve-cvss-vulnerability/ |
| Does Australian Government provide any Cyber Security guidance? | Essentials 8 ISM Australian Privacy Principles. IRAP Australian Energy Sector Cyber Security Framework (AESCSF) |
| What is the Purdue Model? | https://www.zscaler.com/resources/security-terms-glossary/what-is-purdue-model-ics-security |
| Ask questions based on the SANs Posters | – SANs Windows Forensic – https://www.sans.org/posters/windows-forensic-analysis/ – SANS Hunt Evil – https://www.sans.org/posters/hunt-evil/ |
| Explain Cross site Scripting? | Cross site scripting (XSS) is an attack in which an attacker injects malicious executable scripts into the code of a trusted application or website. Attackers often initiate an XSS attack by sending a malicious link to a user and enticing the user to click it. |
| What is a Drive by download? | Lurk, a cybercriminal group infamous for their stealthy and fileless infection techniques, exploited web browser vulnerabilities for their drive-by download attacks. A cyberespionage group called Patchwork (or Dropping Elephant), used drive-by download techniques — such as creating a fake social video website called YoukuTudou to target victims in China — to download and execute an xRAT Trojan under the guise of an Adobe Flash Player update. |
| Explain SQL Injection How do you stop SQL injection? | Structured Query Language (SQL*) Injection is a code injection technique used to modify or retrieve data from SQL databases. By inserting specialized SQL statements into an entry field, an attacker is able to execute commands that allow for the retrieval of data from the database, the destruction of sensitive data, or other manipulative behaviors. Escape All User Supplied Input – When writing SQL, specific characters or words have particular meaning. For example, the ‘*’ character means “any” and the words “OR” is a conditional. To circumvent users who enter these characters either accidentally or maliciously into an API request to the database, user supplied input can be escaped. Escaping a character is the way of telling the database not to parse it as a command or conditional but instead treat it as literal input. Use of Stored Procedures – Although not a robust security strategy by itself, stored procedures can help limit the risk associated with SQL injection. By properly limiting the permissions of the database account running SQL queries, even non-robust application code that is vulnerable to SQL injection will lack the permissions necessary to manipulate unrelated database tables. Stored procedures may also check the type of input parameters, preventing data to be input that violates the type the field is designed to receive. In instances where static queries are insufficient, stored procedures are typically to be avoided. Enforce Least Privilege – As a general rule, in all instances where a website needs to use dynamic SQL, it is important to reduce the exposure to SQL injection by limiting permissions to the narrowest scope required to execute the relevant query. In its most obvious form, this means that an administrative account should in no instance be executing SQL commands as a result of a API call from an unauthorized request. While stored procedures are best utilized for static queries, enforcing least privilege can help reduce the risks of dynamic SQL queries. https://www.cloudflare.com/learning/security/threats/sql-injection/ |
| What is CSRF? | Cross-Site Request Forgery (CSRF) is an attack that forces an end user to execute unwanted actions on a web application in which they’re currently authenticated. XSS Cross Site ScriptingCross-Site Scripting (XSS) attacks are a type of injection, in which malicious scripts are injected into otherwise benign and trusted websites. XSS attacks occur when an attacker uses a web application to send malicious code, generally in the form of a browser side script, to a different end user. Flaws that allow these attacks to succeed are quite widespread and occur anywhere a web application uses input from a user within the output it generates without validating or encoding it. |
| Explain Durability? | |
| Building a Corporate Security Program From The Ground Up? | https://kanenarraway.com/posts/building-corporate-security/ |
| Stateful vs. Stateless Firewalls? | Stateless firewalls are designed to protect networks based on static information such as source and destination. Whereas stateful firewalls filter packets based on the full context of a given network connection, Stateless firewalls filter packets based on the individual packets themselves |
| What is DMARC? | Domain-based Message Authentication, Reporting and Conformation) |
| What is AuditD? | Auditd is the userspace component to the Linux Auditing System. Auditd is short for Linux Audit Daemon. In Linux, daemon is referred to as background running service and there is a ‘d’ attached at the end of the application service as it runs in the background. The job of auditd is to collect and write log files of audit to the disk as a background service https://linuxhint.com/auditd_linux_tutorial/ |
| Explain SQL Joins | |
| What is the difference between Truncate database and drop table? | quickly removes all data from a table, typically bypassing a number of integrity enforcing mechanisms. dropping a table. Deleting a table will result in loss of complete information stored in the table |
| Explain Public Key Cryptography (PKI) | Public key infrastructure (PKI) governs the issuance of digital certificates to protect sensitive data, provide unique digital identities for users, devices and applications and secure end-to-end communications. https://www.keyfactor.com/resources/what-is-pki/ |
| What is the meaning of TCP and IP in the term TCP/IPTransmission Control Protocol/Internet Protocol | TCP/IP Transmission Control Protocol/Internet Protocol TCP/IP stands for Transmission Control Protocol/Internet Protocol and is a suite of communication protocols used to interconnect network devices on the internet. TCP/IP is also used as a communications protocol in a private computer network (an intranet or extranet). |
| What is symmetric and asymmetric | securityhttps://www.ssl2buy.com/wiki/symmetric-vs-asymmetric-encryption-what-are-differences |
| Docker Machine Learning Block Chain Pre vs Post Routing | |
| What is SElinux | http://www.howtogeek.com/135392/htg-explains-why-you-dont-need-an-antivirus-on-linux-and-when-you-do/ |
| Explain Logon types | https://techgenix.com/tgwordpress/wp-content/uploads/2017/02/logon_types_combined.pdf |
| MITM attack happens when a communication between two parties is intruded or intercepted by an outside entity. – Use encryption (public key encryption) between both parties – Avoid using open wi-fi networks. – Use HTTPS, forced TLS or VPN. | |
| What the difference between RFI vs LFIRemote File Inclusion (RFI) is a type of vulnerability most often found on PHP running websites. Local File Inclusion (LFI) is very much like RFI; the only difference is that in LFI the attacker has to upload the malicious script to the target server to be executed locally. https://www.radware.com/security/ddos-knowledge-center/ddospedia/rfi-lfi#:~:text=Remote%20File%20Inclusion%20(RFI)%20is,found%20on%20PHP%20running%20websites.&text=Local%20File%20Inclusion%20(LFI)%20is,server%20to%20be%20executed%20locally. | |
| What are Linux C groups Control groups, usually referred to as cgroups, are a Linux kernel feature which allow processes to be organized into hierarchical groups whose usage of various types of resources can then be limited and monitored. The kernel’s cgroup interface is provided through a pseudo-filesystem called cgroupfs. Grouping is implemented in the core cgroup kernel code, while resource tracking and limits are implemented in a set of per-resource-type subsystems (memory, CPU, and so on). | |
| What is the Shadow Group? | The shadow group allows system programs which require access the ability to read the /etc/shadow file. No users should be assigned to the shadow group. https://www.tenable.com/audits/items/CIS_Oracle_Linux_8_Workstation_L1_v1.0.1.audit:84e2ff94299ade0bea5c704c6904d372 |
| What is kerberos rosting? | Kerberoasting is a post-exploitation attack technique that attempts to crack the password of a service account within the Active Directory (AD). https://www.crowdstrike.com/cybersecurity-101/kerberoasting/#:~:text=Kerberoasting%20is%20a%20post%2Dexploitation,the%20Active%20Directory%20(AD). |
| Common Ports |  |
| What is OWASP? | 1. Broken Access Links 2. Cryptographic Failures 3, Injection 4. Insecure Design 5. Security Misconfiguration 6. Vulnerable and Outdate Components 7. Software and Data Integrity Failures 8. Security Logging and Monitoring. 9. Server-Side Request Forgery (SSRF) 10. XML External Entities (XXE) 11. Cross-Site Scripting (XSS) 12. 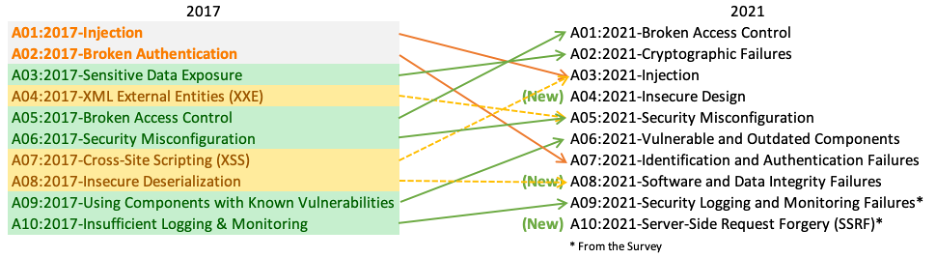 A01:2021-Broken Access Control moves up from the fifth position to the category with the most serious web application security risk; the contributed data indicates that on average, 3.81% of applications tested had one or more Common Weakness Enumerations (CWEs) with more than 318k occurrences of CWEs in this risk category. The 34 CWEs mapped to Broken Access Control had more occurrences in applications than any other category. A02:2021-Cryptographic Failures shifts up one position to #2, previously known as A3:2017-Sensitive Data Exposure, which was broad symptom rather than a root cause. The renewed name focuses on failures related to cryptography as it has been implicitly before. This category often leads to sensitive data exposure or system compromise. A03:2021-Injection slides down to the third position. 94% of the applications were tested for some form of injection with a max incidence rate of 19%, an average incidence rate of 3.37%, and the 33 CWEs mapped into this category have the second most occurrences in applications with 274k occurrences. Cross-site Scripting is now part of this category in this edition. A04:2021-Insecure Design is a new category for 2021, with a focus on risks related to design flaws. If we genuinely want to “move left” as an industry, we need more threat modeling, secure design patterns and principles, and reference architectures. An insecure design cannot be fixed by a perfect implementation as by definition, needed security controls were never created to defend against specific attacks. A05:2021-Security Misconfiguration moves up from #6 in the previous edition; 90% of applications were tested for some form of misconfiguration, with an average incidence rate of 4.5%, and over 208k occurrences of CWEs mapped to this risk category. With more shifts into highly configurable software, it’s not surprising to see this category move up. The former category for A4:2017-XML External Entities (XXE) is now part of this risk category. A06:2021-Vulnerable and Outdated Components was previously titled Using Components with Known Vulnerabilities and is #2 in the Top 10 community survey, but also had enough data to make the Top 10 via data analysis. This category moves up from #9 in 2017 and is a known issue that we struggle to test and assess risk. It is the only category not to have any Common Vulnerability and Exposures (CVEs) mapped to the included CWEs, so a default exploit and impact weights of 5.0 are factored into their scores. A07:2021-Identification and Authentication Failures was previously Broken Authentication and is sliding down from the second position, and now includes CWEs that are more related to identification failures. This category is still an integral part of the Top 10, but the increased availability of standardized frameworks seems to be helping. A08:2021-Software and Data Integrity Failures is a new category for 2021, focusing on making assumptions related to software updates, critical data, and CI/CD pipelines without verifying integrity. One of the highest weighted impacts from Common Vulnerability and Exposures/Common Vulnerability Scoring System (CVE/CVSS) data mapped to the 10 CWEs in this category. A8:2017-Insecure Deserialization is now a part of this larger category. A09:2021-Security Logging and Monitoring Failures was previously A10:2017-Insufficient Logging & Monitoring and is added from the Top 10 community survey (#3), moving up from #10 previously. This category is expanded to include more types of failures, is challenging to test for, and isn’t well represented in the CVE/CVSS data. However, failures in this category can directly impact visibility, incident alerting, and forensics. A10:2021-Server-Side Request Forgery is added from the Top 10 community survey (#1). The data shows a relatively low incidence rate with above average testing coverage, along with above-average ratings for Exploit and Impact potential. This category represents the scenario where the security community members are telling us this is important, even though it’s not illustrated in the data at this time. |
| What is eBFP? | BPF is a revolutionary technology with origins in the Linux kernel that can run sandboxed programs in an operating system kernel. It is used to safely and efficiently extend the capabilities of the kernel without requiring to change kernel source code or load kernel modules. Historically, the operating system has always been an ideal place to implement observability, security, and networking functionality due to the kernel’s privileged ability to oversee and control the entire system. At the same time, an operating system kernel is hard to evolve due to its central role and high requirement towards stability and security. The rate of innovation at the operating system level has thus traditionally been lower compared to functionality implemented outside of the operating system. https://ebpf.io/ |
| What is micro-segmentation? | |
| What is a ‘Golden Ticket’ | https://blog.quest.com/golden-ticket-attacks-how-they-work-and-how-to-defend-against-them/ https://www.cloudflare.com/en-gb/learning/dns/what-is-dns/ |
| What is ‘Ring 0’ | Ring 0 (most privileged) and 3 (least privileged) Ring 0 is accessible to the kernel, which is a central part of most operating systems and can access everything. Code running here is said to be running in kernel mode. Processes running in kernel mode can affect the entire system; if anything fails here, it will probably result in a system shutdown. This ring has direct access to the CPU and the system memory, so any instructions requiring the use of either will be executed here. Ring 3, the least priviliged ring, is accessible to user processes that are running in user mode. This is where most applications running on your computer will reside. This ring has no direct access to the CPU or memory, and therefore has to pass any instructions involving these to ring 0. https://www.futurelearn.com/info/courses/computer-systems/0/steps/53514  |
| How does HTTP maintain state? | HTTP is a stateless (or non-persistent) protocol. Each request is treated by its own. A request will not know what was done in the previous requests. The protocol is designed to be stateless for simplicity. However, some Internet applications, such as e-commerce shopping cart, require the state information to be passed one request to the next. Since the protocol is stateless, it is the responsibility of the application to maintain state information within their application. A few techniques can be used to maintain state information across multiple HTTP requests, namely, – Cookie – Hidden fields of the HTML form. – URL rewriting. https://www3.ntu.edu.sg/home/ehchua/programming/webprogramming/HTTP_StateManagement.html#:~:text=HTTP%20is%20a%20stateless%20(or,to%20be%20stateless%20for%20simplicity. |
| Does TLS use Asymmetric or Symmetric Encryption? | SSL/TLS uses both asymmetric and symmetric encryption to protect the confidentiality and integrity of data-in-transit. Asymmetric encryption is used to establish a secure session between a client and a server, and symmetric encryption is used to exchange data within the secured session. https://www.youtube.com/watch?v=cuR05y_2Gxc |
| What is Asymmetric or Symmetric Encryption? | Symmetric encryption uses a single key that needs to be shared among the people who need to receive the message while asymmetric encryption uses a pair of public key and a private key to encrypt and decrypt messages when communicating. https://www.ssl2buy.com/wiki/symmetric-vs-asymmetric-encryption-what-are-differences#:~:text=Symmetric%20encryption%20uses%20a%20single,and%20decrypt%20messages%20when%20communicating. |
| What is the difference between General Purpose OS and other operating systems like ESXi? | https://www.linkedin.com/pulse/policy-process-procedure-what-difference-khalil-al-qaheri/ |
| Explain SHA-11 algorithm in detail? | https://www.geeksforgeeks.org/sha-1-hash-in-java/#:~:text=SHA%2D1%20or%20Secure%20Hash,which%20is%2040%20digits%20long. |
| What is MD5 checksum? | MD5 (technically called MD5 Message-Digest Algorithm) is a cryptographic hash function whose main purpose is to verify that a file has been unaltered. Instead of confirming two sets of data are identical by comparing the raw data, MD5 does this by producing a checksum on both sets and then comparing the checksums to verify they’re the same. MD5 has certain flaws, so it isn’t useful for advanced encryption applications, but it’s perfectly acceptable to use it for standard file verifications. |
| Explain sessions hijacking and the effect of 2 factor authentication? | https://medium.com/@fatihucar/effectiveness-of-two-factor-authentication-for-preventing-fraudulent-transactions-during-session-5a00da7264ce https://sec.okta.com/sessioncookietheft https://www.knowbe4.com/hubfs/KB4-CON2019-12WaystoHack2FA.pdf |
| What is MITRE | MITRE ATT&CK® is a globally-accessible knowledge base of adversary tactics and techniques based on real-world observations. The ATT&CK knowledge base is used as a foundation for the development of specific threat models and methodologies in the private sector, in government, and in the cybersecurity product and service community. |
| What’s the difference between a policy, process and procedure? | https://www.linkedin.com/pulse/policy-process-procedure-what-difference-khalil-al-qaheri/ |
| Explain Zero Trust | Zero trust network access (ZTNA) is a product or service that creates an identity- and context-based, logical access boundary around an application or set of applications. The applications are hidden from discovery, and access is restricted via a trust broker to a set of named entities. https://www.gartner.com/en/information-technology/glossary/zero-trust-network-access-ztna-#:~:text=Zero%20trust%20network%20access%20(ZTNA)%20is%20a%20product%20or%20service,a%20set%20of%20named%20entities. |
| Name 3 Internet Protocols which use TCP? Name 3 protocols which use udp? Name 2 which use neither? | FTP/HTTP/SSH VOIP/ICMP echo/DDOS/NTP/DNS https://osi-model.com/ |
| What is the difference between encoding, encryption and hashing? | Encoding: Reversible transformation of data format, used to preserve the usability of data. Hashing: A one-way summary of data that cannot be reversed and is used to validate the integrity of data. Encryption: Secure encoding of data used to protect the confidentiality of data. |
| What is a rainbow table? | A rainbow table attack is a password cracking method that uses a special table (a “rainbow table”) to crack the password hashes in a database https://www.geeksforgeeks.org/understanding-rainbow-table-attack/ |
| If you had to encrypt and compress data during transmition, what would you do first? | You should compress before encrypting. Encryption turns your data into high-entropy data, usually indistinguishable from a random stream. Compression relies on patterns in order to gain any size reduction. |
| Cross site request forgery (CSRF), also known as XSRF, Sea Surf or Session Riding, is an attack vector that tricks a web browser into executing an unwanted action in an application to which a user is logged in. https://www.imperva.com/learn/application-security/csrf-cross-site-request-forgery/ | |
| In a public-key cryptography, you have a public and a private key, and you often perform both encryption and signing functions. Which key is used for which purpose? | https://www.cloudflare.com/en-gb/learning/ssl/how-does-public-key-encryption-work/ |
| Explain AWS Security and networking | VPC Security Groups Network ACls https://docs.aws.amazon.com/vpc/latest/userguide/vpc-network-acls.html |
| Explain Kubernetes networking? | Kubernetes automates operational tasks of container management and includes built-in commands for deploying applications, rolling out changes to your applications, scaling your applications up and down to fit changing needs, monitoring your applications, and more—making it easier to manage applications. Kubernetes networking allows Kubernetes components to communicate with each other and with other applications. The Kubernetes platform is different from other networking platforms because it is based on a flat network structure that eliminates the need to map host ports to container ports. The Kubernetes platform provides a way to run distributed systems, sharing machines between applications without dynamically allocating ports. Kubernetes is a portable, extensible, open source platform for managing containerized workloads and services, that facilitates both declarative configuration and automation. It has a large, rapidly growing ecosystem. Kubernetes services, support, and tools are widely available. The name Kubernetes originates from Greek, meaning helmsman or pilot. K8s as an abbreviation results from counting the eight letters between the “K” and the “s”. Google open-sourced the Kubernetes project in 2014. Kubernetes combines over 15 years of Google’s experience running production workloads at scale with best-of-breed ideas and practices from the community. Containers uses a Flat network. https://kubernetes.io/docs/concepts/overview/ |
| What are Helm Charts | Helm helps you manage Kubernetes applications — Helm Charts help you define, install, and upgrade even the most complex Kubernetes application. Charts are easy to create, version, share, and publish — so start using Helm and stop the copy-and-paste. Helm is a graduated project in the CNCF and is maintained by the Helm community. |
| Explain how to achieve lateral movement? | https://www.crowdstrike.com/cybersecurity-101/lateral-movement/ |
| Explain a tool to gain privilege escalation? | Benjamin Delpy originally created Mimikatz as a proof of concept to show Microsoft that its authentication protocols were vulnerable to an attack. Instead, he inadvertently created one of the most widely used and downloaded threat actor tools of the past 20 years. https://www.varonis.com/blog/what-is-mimikatz#do |
| What is side car? | A sidecar is a separate container that runs alongside an application container in a Kubernetes pod – a helper application of sorts. Typically, the sidecar is responsible for offloading functions required by all apps within a service mesh – SSL/mTLS, traffic routing, high availability, and so on – |
| Familiarise your self with Flare-On 9 Challenge Solutions | https://www.mandiant.com/resources/blog/flareon9-challenge-solutions |
| Difference between TLS version 1.2 and 1.3. Explain the DNS flow when any website is accessed on browser. | TLS 1.3 offers several improvements over earlier versions, most notably a faster TLS handshake and simpler, more secure cipher suites. Zero Round-Trip Time (0-RTT) key exchanges further streamline the TLS handshake. Together, these changes provide better performance and stronger security. A Faster TLS Handshake TLS encryption and SSL decryption require CPU time and add latency to network communications, somewhat degrading performance. Under TLS 1.2, the initial handshake was carried out in clear text, meaning that even it needed to be encrypted and decrypted. Given that a typical handshake involved 5 – 7 packets exchanged between the client and server, this added considerable overhead to the connection. Under version 1.3, server certificate encryption was adopted by default, making it possible for a TLS handshake to be performed with 0 – 3 packets, reducing or eliminating this overhead and allowing faster, more responsive connections. Simpler, Stronger Cipher Suites In addition to reducing the number of packets to be exchanged during the TLS handshake, version 1.3 has also shrunk the size of the cipher suites used for encryption. In TLS 1.2 and earlier versions, the use of ciphers with cryptographic weaknesses had posed potential security vulnerabilities. TLS 1.3 includes support only for algorithms that currently have no known vulnerabilities, including any that do not support Perfect Forward Secrecy (PFS). The update has also removed the ability to perform “renegotiation,” in which a client and server that already have a TLS connection can negotiate new parameters and generate new keys, a function that can increase risk. Zero Round-Trip Time (0-RTT) As with SSL, TLS relies on key exchanges to establish a secure session. In earlier versions, keys could be exchanged during the handshake using one of two mechanisms: a static RSA key, or a Diffie-Hellman key. In TLS 1.3, RSA has been removed, along with all static (non-PFS) key exchanges, while retaining ephemeral Diffie-Hellman keys. In addition to eliminating the security risk posed by a static key, which can compromise security if accessed illicitly, relying exclusively on the Diffie-Hellman family allows the client to send the requisite randoms and inputs needed for key generation during its “hello.” By eliminating an entire round-trip on the handshake, this saves time and improves overall site performance. In addition, when accessing a site that has been visited previously, a client can send data on the first message to the server by leveraging pre-shared keys (PSK) from the prior session—thus “zero round-trip time” (0-RTT). https://www.a10networks.com/glossary/key-differences-between-tls-1-2-and-tls-1-3 |
| Packet flow for networking and security | o transfer a packet from source to destination, both the MAC address and IP address of the destination should be known. If the destination MAC address is not present then ARP will resolve this issue first then the packet will be delivered to a destination host. There are simple rules for a packet flow in a network: If the destination host is present in the same network as the source host then the packet will be delivered directly to the destination host using MAC address. Within a network, the packet will be delivered on the basis of MAC address. MAC address never crosses its broadcast domain. Now, first, we have to take an idea about ARP. https://www.geeksforgeeks.org/packet-flow-in-the-same-network/ |
| What is Perfect Forward Secrecy Definition? | Perfect Forward Secrecy (PFS), also called forward secrecy (FS), refers to an encryption system that changes the keys used to encrypt and decrypt information frequently and automatically. This ongoing process ensures that even if the most recent key is hacked, a minimal amount of sensitive data is exposed. Web pages, calling apps, and messaging apps all use encryption tools with perfect forward secrecy that switch their keys as often as each call or message in a conversation, or every reload of an encrypted web page. This way, the loss or theft of one decryption key does not compromise any additional sensitive information—including additional keys. https://avinetworks.com/glossary/perfect-forward-secrecy/ |
| OWSAP Top 10 |  |
| Explain Log4J | |
| How can you Pentest a WAF based Application | Default no configuration settings – No WaF protection at all. Simple URL restriction policy – Restrictions for URL access only. Simple URL restrictions & parameter checking – URL restriction and parameter inspection. Simple URL restrictions & parameter checking for basic HTTP traffic – All the above with specific malicious traffic inspection (this will be listed below in the attack types). Simple URL restrictions & parameter checking for basic JSON/SOAP specific traffic – Same as the above, however, may also be required if your application uses specific web services. File upload checking – finally, file upload facilities should be inspected for malicious content. Popular attack signatures – encoded and non-encoded SQL injection, XSS, OS Injection, LDAP Injection, XML Injection, Path Traversal, Local File Inclusion, Remote File Inclusion etc. Header manipulation techniques – attacking cookie/referer/host headers etc. JSON/SOAP schema bypass techniques. Masked data – shikata_ga_nai and Base64 encoding etc. File scanning manipulation – masked and unmasked anti-virus and malware signatures. Charecter limit oversights Finger printing WAF SQL injection, Cross-Site Scripting (XSS), buffer overflows, file inclusion attacks https://owasp.org/www-pdf-archive/OWASP_Stammtisch_Frankfurt_WAF_Profiling_and_Evasion.pdf |
| What is the MS GINA | Winlogon, the GINA, and network providers are the parts of the interactive logon model. The interactive logon procedure is normally controlled by Winlogon, MSGina.dll, and network providers. To change the interactive logon procedure, MSGina.dll can be replaced with a customized GINA DLL |
| Explain how a VPN works? |  |
Explain Threat Modellingl
Explain STRIDE
Explain DevSecOps and SDLC
Explain what is a Security Strategy
What is BIA
What is Risk Management?
What is FIRST method?

| Threat Modelling: | Threat modeling is a systematic approach used to identify, assess, and mitigate potential threats and vulnerabilities in a system, application, or process. It involves analyzing the system’s architecture, identifying potential threats, and evaluating their potential impact. The goal is to proactively identify and address security risks, enabling organizations to design and implement effective security controls. |
| STRIDE | STRIDE is an acronym that represents different categories of threats used in threat modeling. It stands for: – Spoofing An attacker impersonates a legitimate user or system to gain unauthorized access – Tampering, Unauthorized modification or alteration of data, code, or system components -Repudiation, The inability to prove or disprove an action or event, often used by attackers to deny their involvement. – Information Disclosure: Unauthorized access to sensitive or confidential information. – Denial of Service: Disrupting or disabling the availability or functionality of a system or service. – Elevation of Privilege: An attacker gains unauthorized privileges or elevated access rights. By considering each of these threat categories during threat modeling, organizations can identify potential security weaknesses and develop appropriate countermeasures. |
| DevSecOps | DevSecOps and SDLC: DevSecOps is an approach that integrates security practices into the software development lifecycle (SDLC) from the beginning, rather than treating security as an afterthought. It emphasizes collaboration between development, operations, and security teams to ensure that security considerations are addressed at every stage of the software development process. |
| SDLC | The SDLC refers to the series of phases and activities involved in developing software, from conception to retirement. It typically includes requirements gathering, design, development, testing, deployment, and maintenance. When security is incorporated into the SDLC, it ensures that security measures are implemented at each stage, reducing vulnerabilities and enhancing overall system security |
| Security Strategy | A security strategy is a comprehensive plan that outlines an organization’s approach to managing and mitigating security risks. It includes a set of guiding principles, objectives, and measures to protect critical assets, data, and systems. A security strategy typically covers areas such as risk assessment, incident response, access control, threat prevention, and employee awareness and training. The strategy is tailored to the organization’s specific needs, considering factors such as industry regulations, business goals, and the threat landscape. It provides a roadmap for implementing security controls and establishes a framework for ongoing monitoring, evaluation, and improvement of security measures. |
| BIA | BIA (Business Impact Analysis): Business Impact Analysis is a process used to identify and evaluate the potential impact of a disruption or incident on critical business operations. It assesses the potential financial, operational, and reputational consequences of various events, such as natural disasters, cyber-attacks, or system failures. BIA involves identifying key business processes, determining their criticality and dependencies, and estimating the potential impacts of disruptions, including financial losses, customer dissatisfaction, and regulatory non-compliance. The analysis helps prioritize the allocation of resources for disaster recovery planning, business continuity strategies, and risk mitigation efforts. |
| Risk Management | Risk management is the process of identifying, assessing, and prioritizing risks to minimize their impact on an organization’s objectives. It involves understanding potential threats and vulnerabilities, analyzing their likelihood and potential impact, and developing strategies to mitigate or transfer the risks. The risk management process typically includes risk identification, risk assessment, risk mitigation planning, risk monitoring, and risk review. It aims to strike a balance between risk reduction and business goals, enabling organizations to make informed decisions and allocate resources effectively to address security threats. |
| FIRST Method | The FIRST (Forum of Incident Response and Security Teams) method is a framework used for incident response. It provides a structured approach to handling security incidents effectively and efficiently. The FIRST method consists of the following steps: |
| What is the Kubernetes command line tool, and what does it do? | Kubectl, this allows you to run commands against your Kubernetes clusters |
| What is a control plane? | The brain of the Kubernetes cluster. It contains several components like the API server, which acts as a gateway to the cluster, the scheduler, which assigns workloads to nodes, and the controller manager, which manages various controllers to maintain desired state of the cluster. Resides on designated node in the cluster |
| What is the kubectl command to view all CBContainer resources? | kubectl get all -n cbcontainers-dataplane |
| What are the two K8’s processes that you will find running on all of your K8’s nodes? | Kubeproxy and kubelet |
| What is a secret in containerization? | A secret refers to a sensitive piece of information or confidential data that is securely stored and managed for use by applications running within containers. Secrets are typically used to handle sensitive information, such as API keys, passwords, or other authentication creden |
| What are some risks associated with Containers and Kubernetes | Third party image registries -> Attackers target these and insert malicious code- Ephemeral nature of containers- > Makes it more challenging to monitor and detect vulnerabilities- Speed of deployment -> Modern apps are updated rapidly which means that rigorous testing and scanning is required to prevent vulnerabilities in prod environments- Complexity of environments, difficult for any one person to understand it |
| What Kubernetes hardening rules modules are used to restrict the capabilities of individual programs and containers, confining them to a specific set of permissions and limiting their access to system resources? | Confidential │© Carbon Black7AppArmor, SELinux, SecComp Profile |
| What is a POD | A pod is the smallest deployable unit in Kubernetes and is the basic building block of the Kubernetes object model. Basically, a pod is a group of one or more containers with shared storage and network resources, and a specification for how to run the containers. Pods run on nodes. If a pod (or the nodes it runs on) fails, Kubernetes can automatically create a new replica of that pod to continue operations. Pods are used for deploying and m |
| What is a container image? | A container image is a lightweight, standalone, and executable software package that includes everything needed to run a piece of software including code, runtime, libraries, and system tools. It is a static and immutable file, meaning it cannot be changed. A container image has a very basic operating system only to run its application within the container. W |
| What is a container? | A container is a running instance of a container image. It is a runnable process that encapsulates the application and its dependencies. When a container is started, it runs the code and processes defined in the container image. Container creation also adds a writable layer on top of the container image. |
| What is the writable layer in a container? | When a container starts, it creates what we call a writable layer. This is also referred to as the container layer. This writable layer, known as the container’s file system, allows processes running inside the container to make changes, create files, modify |
| Does the writable layer affect the container image | No, the underlying image remains immutable and unchanged. And modifications or changes made within the running container are stored in the writable layer on top of the container image |
| What are some IRL scenarios where changes would be made to a container’s writable layer? | Confidential │© Carbon Black14Application logs, database data updates, temporary files/caches, configuration overrides, application updates |
| Explain Email Security | Sure, here are the top 5 email security interview questions with their answers: 1. What are the common types of email attacks, and how can they be mitigated? Answer: Common types of email attacks include phishing, spear-phishing, Business Email Compromise (BEC), and malware distribution. Phishing: Use email filtering solutions to detect and block phishing emails. Educate users about recognizing suspicious emails. Spear-phishing: Implement multi-factor authentication (MFA) and train employees to verify unusual requests, especially those involving financial transactions. Business Email Compromise (BEC): Use email authentication protocols like SPF, DKIM, and DMARC to prevent email spoofing. Conduct regular security awareness training. Malware distribution: Employ advanced threat protection that includes sandboxing to detect and block malicious attachments and links. 2. How does SPF, DKIM, and DMARC work together to secure email? Answer: SPF (Sender Policy Framework): Validates that the email comes from an authorized server. The domain owner publishes an SPF record specifying which IP addresses are allowed to send emails on its behalf. DKIM (DomainKeys Identified Mail): Adds a digital signature to emails. This signature allows the recipient’s server to verify that the email was indeed sent by the domain owner and was not altered in transit. DMARC (Domain-based Message Authentication, Reporting & Conformance): Uses SPF and DKIM to determine the authenticity of an email. Domain owners publish DMARC policies in their DNS records to instruct receiving servers on how to handle emails that fail SPF or DKIM checks and provide reports on email delivery and authentication statistics. When combined, these protocols help to prevent spoofing and phishing by ensuring that only legitimate emails are delivered. 3. What steps would you take to secure an organization’s email infrastructure? Answer: Implement Email Filtering: Use email security gateways to filter out spam, phishing, and malware. Enable Email Authentication: Configure SPF, DKIM, and DMARC to authenticate email senders. Use Encryption: Ensure emails are encrypted in transit using TLS and, where necessary, use end-to-end encryption. Conduct Security Awareness Training: Educate employees on recognizing phishing attempts and the importance of email security. Regularly Update Systems: Keep email servers and security software up to date with the latest patches. Implement Multi-Factor Authentication (MFA): Require MFA for email account access to add an extra layer of security. Monitor and Respond: Continuously monitor email traffic for suspicious activity and have an incident response plan in place. 4. What is Business Email Compromise (BEC) and how can organizations protect against it? Answer: Business Email Compromise (BEC) is a type of email attack where attackers impersonate a trusted entity, such as a company executive or business partner, to trick employees into making unauthorized transfers of funds or sensitive data. Protection Measures: User Education: Train employees to recognize and report suspicious emails and verify unusual requests through a different communication channel. Email Authentication: Use SPF, DKIM, and DMARC to prevent email spoofing. MFA: Implement multi-factor authentication for accessing email accounts. Policies and Procedures: Establish and enforce policies for verifying financial and sensitive information requests. Email Filtering: Use advanced threat protection to detect and block BEC attempts. 5. How can an organization handle phishing email incidents? Answer: Identification and Reporting: Ensure employees know how to identify and report phishing emails. Use automated tools to flag suspicious emails. Containment: Immediately block the sender and isolate affected systems to prevent the spread of any potential malware. Investigation: Analyze the phishing email to understand its origin and intent. Check if any sensitive information was compromised. Remediation: Remove the phishing email from all affected mailboxes. Reset passwords and review access logs for any unauthorized activity. Communication: Inform affected users about the incident and provide guidance on how to handle similar threats in the future. Training: Update training programs based on the incident to improve user awareness and response. Review and Improve: Regularly review and update email security policies and technologies to enhance protection against future phishing attempts. These questions and answers should help you prepare for an email security interview effectively. Secure Email Gateways (SEGs) employ various technology methods to secure emails. Here are the top 5: 1. Spam and Phishing Filtering Description: SEGs use advanced algorithms and threat intelligence to detect and block spam and phishing emails. How it works: They analyze email content, sender reputation, and email patterns to identify and quarantine malicious emails before they reach the end-user. 2. Malware Detection and Prevention Description: SEGs incorporate anti-malware engines to scan and block emails containing malicious attachments or links. How it works: They use signature-based detection, heuristic analysis, and sandboxing to identify known and unknown malware threats. 3. Email Encryption Description: Encryption ensures that emails are secure during transit and can only be read by the intended recipient. How it works: SEGs use protocols like TLS (Transport Layer Security) for encrypting emails in transit and may offer end-to-end encryption for highly sensitive communications. 4. Content Filtering and Data Loss Prevention (DLP) Description: SEGs can scan emails for sensitive or confidential information and prevent unauthorized data leaks. How it works: They use predefined policies and content analysis to detect and block emails containing sensitive data like credit card numbers, social security numbers, or proprietary information. 5. Email Authentication (SPF, DKIM, DMARC) Description: SEGs support email authentication protocols to verify the legitimacy of email senders and prevent spoofing. How it works: SPF (Sender Policy Framework): Verifies if an email is sent from an authorized IP address. DKIM (DomainKeys Identified Mail): Uses digital signatures to ensure the email has not been tampered with. DMARC (Domain-based Message Authentication, Reporting & Conformance): Provides a policy framework for how to handle emails failing SPF or DKIM checks and offers reporting capabilities. These technologies collectively enhance email security by preventing unauthorized access, detecting and blocking threats, and ensuring the integrity and confidentiality of email communications. 6. URL Protection and Link Analysis Description: SEGs provide protection against malicious URLs embedded in emails. How it works: They scan and analyze URLs in real-time to detect and block access to phishing sites or sites hosting malware. This can involve rewriting URLs to route through secure servers that check the destination before allowing users to proceed. Additionally, SEGs often use threat intelligence databases to identify and block known malicious links. 7. Advanced Threat Protection (ATP) Description: ATP involves sophisticated techniques to detect and mitigate advanced email threats such as zero-day exploits, targeted attacks, and other sophisticated malware. How it works: Behavioral Analysis: Monitors the behavior of attachments and links in a sandbox environment to detect malicious activity. Machine Learning: Uses machine learning algorithms to identify and predict new and evolving threats by analyzing patterns and anomalies. Threat Intelligence Integration: Leverages global threat intelligence feeds to stay updated on the latest threats and adapt defenses accordingly. 8. Outbound Email Protection Description: SEGs not only protect incoming emails but also monitor and secure outgoing emails to prevent data leaks and ensure compliance with regulatory requirements. How it works: DLP Policies: Apply data loss prevention rules to scan outgoing emails for sensitive or confidential information and take actions such as encryption, blocking, or flagging for review. Content Filtering: Analyze the content of outgoing emails to ensure they do not contain inappropriate or unauthorized information. Compliance Checks: Ensure that outgoing emails adhere to industry regulations and corporate policies, automatically applying necessary actions like encryption or archiving. 9. Attachment Sandboxing and Analysis Description: SEGs employ sandboxing technology to safely execute and analyze email attachments in an isolated environment before they reach the recipient. How it works: Isolated Execution: Attachments are opened and executed in a controlled, virtualized environment (sandbox) to observe their behavior. Behavioral Analysis: Monitors for malicious activities such as unusual system changes, network communications, or attempts to exploit vulnerabilities. Threat Detection: If the attachment exhibits suspicious or harmful behavior, it is blocked or quarantined to prevent it from reaching the end-user. 10. Email Continuity Description: Ensures continuous email flow and access even during outages or failures in the primary email system. How it works: Failover Mechanisms: Automatically redirects email traffic to backup servers or cloud-based systems when the primary email server is down. Email Queueing: Temporarily stores emails in a queue if the destination server is unreachable, delivering them once the server is back online. User Access: Provides users with web-based access to their emails during an outage, allowing them to send and receive messages seamlessly until normal operations are restored. 11. Email Archiving and Retrieval Description: Securely stores and manages email communications for long-term retention and easy retrieval. How it works: Archiving Policies: Automatically archives emails based on predefined policies, such as retention periods, compliance requirements, and specific keywords. Storage Solutions: Uses scalable and secure storage solutions to retain large volumes of email data, ensuring data integrity and accessibility. Search and Retrieval: Provides powerful search tools to quickly locate and retrieve archived emails for legal, compliance, or business purposes, ensuring that critical information is always accessible when needed. |
| What is the difference between Phishing and Spear Phishing | Spear phishing emails are a more advanced form of phishing. Spear phishing is a specific and targeted attack on one or a select number of victims, while regular phishing attempts to scam masses of people. In spear phishing, scammers often use social engineering and spoofed emails to target specific individuals in an organization. They may impersonate family members, colleagues, or business acquaintances. |
| How does SPF, DKIM, and DMARC work together to secure email? | SPF (Sender Policy Framework): Validates that the email comes from an authorized server. The domain owner publishes an SPF record specifying which IP addresses are allowed to send emails on its behalf. DKIM (DomainKeys Identified Mail): Adds a digital signature to emails. This signature allows the recipient’s server to verify that the email was indeed sent by the domain owner and was not altered in transit. DMARC (Domain-based Message Authentication, Reporting & Conformance): Uses SPF and DKIM to determine the authenticity of an email. Domain owners publish DMARC policies in their DNS records to instruct receiving servers on how to handle emails that fail SPF or DKIM checks and provide reports on email delivery and authentication statistics. Configuring SPF, DKIM, and DMARC 1. Configuring SPF (Sender Policy Framework) Identify Your Sending IP Addresses: List all IP addresses that are authorized to send emails on behalf of your domain. Create an SPF Record: Construct an SPF record using the identified IP addresses. The format is typically: v=spf1 ip4:192.0.2.0/24 ip4:198.51.100.123 include:_spf.example.com ~allv=spf1 specifies the SPF version.ip4: and ip6: specify the authorized IP addresses.include: allows including SPF records from other domains.~all or -all specifies the policy for handling non-compliant emails (~all is soft fail, -all is hard fail).Publish the SPF Record: Add the SPF record as a TXT record in your domain’s DNS settings. 2. Configuring DKIM (DomainKeys Identified Mail) Generate DKIM Keys: Use your email server or a DKIM tool to generate a public and private key pair. Create a DKIM Record: The public key is published in the DNS as a TXT record. The format is: selector._domainkey.example.com IN TXT "v=DKIM1; k=rsa; p=publicKey"selector is a unique identifier for the key.v=DKIM1 specifies the DKIM version.k=rsa specifies the key type.p=publicKey is the public key generated earlier.Configure the Mail Server: Configure your email server to sign outgoing emails with the private key. Publish the DKIM Record: Add the DKIM TXT record to your domain’s DNS settings. 3. Configuring DMARC (Domain-based Message Authentication, Reporting & Conformance) Create a DMARC Policy: Define your DMARC policy, which includes the policy for handling emails, reporting options, and alignment modes. The format is: v=DMARC1; p=none; rua=mailto:dmarc-reports@example.com; ruf=mailto:forensic-reports@example.com; adkim=s; aspf=sv=DMARC1 specifies the DMARC version.p= specifies the policy (none, quarantine, or reject).rua= specifies the email address for aggregate reports.ruf= specifies the email address for forensic reports.adkim= and aspf= specify the DKIM and SPF alignment modes (s for strict, r for relaxed).Publish the DMARC Record: Add the DMARC record as a TXT record in your domain’s DNS settings at _dmarc.example.com.Example DNS Records SPF Record: example.com. IN TXT "v=spf1 ip4:192.0.2.0/24 include:_spf.example.com ~all"DKIM Record: selector._domainkey.example.com. IN TXT "v=DKIM1; k=rsa; p=MIGfMA0GCSqGSIb3DQEBAQUAA4GNADCBiQKBgQDmE..."DMARC Record: _dmarc.example.com. IN TXT "v=DMARC1; p=none; rua=mailto:dmarc-reports@example.com; ruf=mailto:forensic-reports@example.com; adkim=s; aspf=s"By configuring SPF, DKIM, and DMARC, you can significantly improve your email security, protect against spoofing, and ensure the integrity of your email communications. |
| Explain Zero Trust Concepts | Least Privileged and Continuous Authorization Never trust, always verify |
Explain Email Routing

Questions to ask at the end of interview
- Could you please explain the reason for this open position and what the company hopes to achieve by filling it?”
- Can you provide an overview of the team I’ll be working with and how it fits within the larger organization?”
- What is the onboarding process like for new employees, especially in this position?
- What opportunities are there for cross-functional work or involvement in projects outside of this immediate team?” , Participating in Marketing Events Speaking Engagements or Building CTF, etc
Other resources
- https://www.deepshankaryadav.net/cyber-security-and-dfir-interview-questions/
- https://www.trendmicro.com/vinfo/us/security/definition/a
- https://www.indeed.com/career-advice/interviewing/ccna-interview-questions
- https://www.imperva.com/learn/application-security/
- https://www.crowdstrike.com/cybersecurity-101/
- https://help.zscaler.com/zia
- https://www.hackthebox.com/storage/press/samplereport/sample-penetration-testing-report-template.pdf
- https://www.edureka.co/blog/interview-questions/cybersecurity-interview-questions/

Learning Resources
[1] https://lnkd.in/gkmzQFZ7 Several videos including 2 concerning technical interview questions by Mike Meyers of Total Seminars and Richard Chapman of CyberNow Labs.
[2] https://lnkd.in/g4shgnF8 An article on go-to answers for tricky interview questions; not SOC Analyst specific.
[3] https://lnkd.in/gFWn_TGY 47 Cybersecurity interview questions from Springboard.
[4] https://lnkd.in/gyBN9y_7 50 Cybersecurity interview questions from Edureka.
[5] https://lnkd.in/gUgA2GUQ SOC Analyst interview questions from LetsDefend.
[6] https://lnkd.in/gAAGZHcq What to do before, during, and after an interview from LinkedIn Learning.
[7] https://lnkd.in/gPRKmYd4 I’ve been told I will be asked about OWASP® Foundation Top 10. Here is all you need to answer questions about it from Sucuri Security.
[8] https://lnkd.in/gjdgqE9r A great interview prep resource list courtesy of Will Broom.
[9] https://lnkd.in/g8GV2uuN 12 SOC Analyst interview questions courtesy of 👉🏼 Gerald Auger, Ph.D. Auger, Ph.D. and Simply Cyber.
[10] https://lnkd.in/g5jvXbsM Short, sweet, and great interview advice courtesy of Thrive Global.
[11] https://lnkd.in/gdavh_ni This is a great post covering interview techniques courtesy of David Meece.
[12] https://lnkd.in/g_UhYqCi Some good pre-interview preparation advice courtesy of Josh Fullmer.
Professor Messera – https://www.youtube.com/@professormesser/videos
Learning Resources
- CybraryIT – https://www.cybrary.it/upgrade/
- Rootme_org – https://www.root-me.org/?lang=en
- LetsDeendIO – https://letsdefend.io/
- Hackthebox_eu – https://www.hackthebox.com/
- RealTryHackMe – https://tryhackme.com/
- OverThewireCTF – https://overthewire.org/wargames/
- https://cyberdefenders.org/
More Resources
Top 30 Penetration Tester Interview Questions / Answers
https://lnkd.in/eAkvQFZG
Cyber Security Interview Prep
https://lnkd.in/eky9v_hC
SOC Analyst Interview Questions (LetsDefend)
https://lnkd.in/eqFPGS-Z
GRC Entry-Level Interview Q&A (👉🏼 Gerald Auger, Ph.D.)
https://lnkd.in/eK6uti-W
Mastering the Art of the Interview (TEDX Talks / Ashley Rizzotto, M.Ed.)
https://lnkd.in/ecMGM5Tn
Tell Me About Yourself – A Good Answer To This Question
https://lnkd.in/eES-wF7Q
How to Ace a Job Interview: 10 Crucial Tips
https://lnkd.in/e29vxaH9
Cybersecurity Interview Preparation Playlist (👉 Jon Good 👈)
https://lnkd.in/ek-x4cPx
How To Be Confident In Interviews
https://lnkd.in/eGQgXbKJ
How To Crush Any Interview
https://lnkd.in/eWr2mU57
10 Best Questions to Ask an Interviewer
https://lnkd.in/efMbFn4S
How to Ace Your Job Interview (David Bombal)
https://lnkd.in/eKyqWpCU
Cybersecurity Practice Interview Questions Playlist (Josh Madakor)
https://lnkd.in/eqw-Z-tD
How to Prepare for a Cyber Security Interview (Cyberspatial)
https://lnkd.in/eTzegN6G
How to Fail a Cybersecurity Interview (Cyberspatial)
https://lnkd.in/eu_KyAf2
Interview Tips


Cloud Interview Questions
- interviewing.io
- https://www.youtube.com/@interviewingio/playlists
- https://start.interviewing.io/dashboard/interviewee