Core AWS Networking Services
AWS’s networking suite is a testament to its commitment to providing robust, scalable, and secure networking options for its diverse customer base. These services are designed to meet the dynamic needs of modern enterprises, facilitating seamless connectivity, enhanced security, and efficient data distribution across the globe.

- Amazon CloudFront: This Content Delivery Network (CDN) exemplifies efficiency, delivering content with high transfer speeds and low latency. Integrated with AWS’s infrastructure, CloudFront ensures secure and rapid data delivery worldwide.
- Amazon Virtual Private Cloud (VPC): Amazon VPC offers users a segregated portion of the AWS cloud, granting complete control over the network environment. This service enables precise configuration of IPs, subnets, and gateways, catering to a variety of application hosting needs.
- AWS Direct Connect: By establishing a dedicated network connection from an on-premises data center to AWS, Direct Connect reduces costs and increases bandwidth throughput, enhancing the connectivity between on-premises networks and AWS’s cloud environment.
- Elastic Load Balancing: This service adeptly distributes incoming network traffic across multiple targets, such as EC2 instances, ensuring application resilience and performance stability under varying load conditions.
- Amazon Route 53: A scalable DNS web service, Route 53 efficiently translates domain names into IP addresses, facilitating reliable and cost-effective end-user application routing.

Amazon Virtual Private Cloud (VPC)
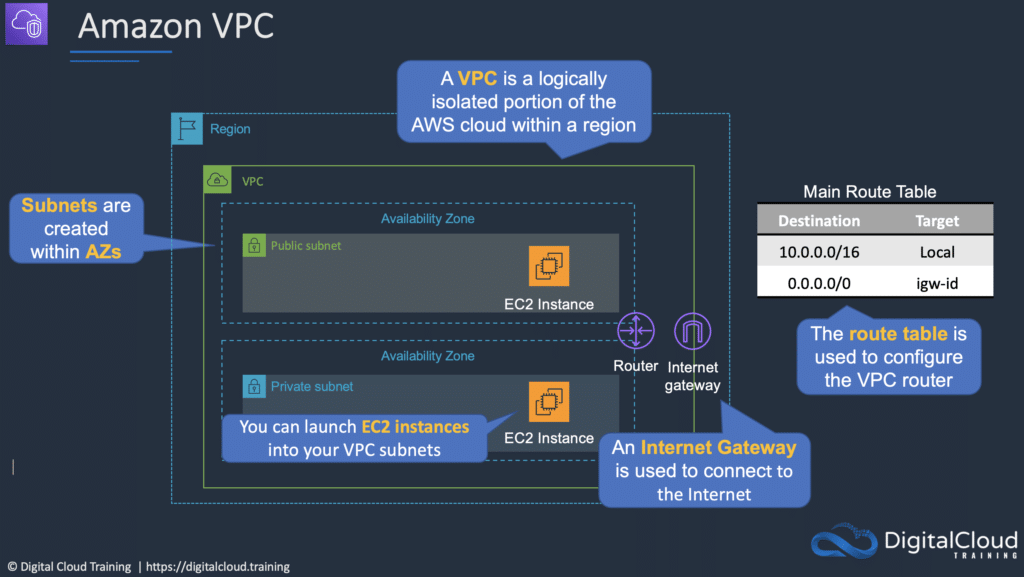
A virtual private cloud (VPC) is a virtual network dedicated to your AWS account. Analogous to having your own DC inside AWS. It is logically isolated from other virtual networks in the AWS Cloud.
Provides complete control over the virtual networking environment including selection of IP ranges, creation of subnets, and configuration of route tables and gateways. You can launch your AWS resources, such as Amazon EC2 instances, into your VPC.
When you create a VPC, you must specify a range of IPv4 addresses for the VPC in the form of a Classless Inter-Domain Routing (CIDR) block; for example, 10.0.0.0/16.
This is the primary CIDR block for your VPC.
A VPC spans all the Availability Zones in the region.
You have full control over who has access to the AWS resources inside your VPC.
You can create your own IP address ranges, and create subnets, route tables and network gateways.
When you first create your AWS account a default VPC is created for you in each AWS region.
A default VPC is created in each region with a subnet in each AZ.
By default you can create up to 5 VPCs per region.
You can define dedicated tenancy for a VPC to ensure instances are launched on dedicated hardware (overrides the configuration specified at launch).
A default VPC is automatically created for each AWS account the first time Amazon EC2 resources are provisioned.
The default VPC has all-public subnets.
Public subnets are subnets that have:
- “Auto-assign public IPv4 address” set to “Yes”.
- The subnet route table has an attached Internet Gateway.
Instances in the default VPC always have both a public and private IP address.
AZs names are mapped to different zones for different users (i.e. the AZ “ap-southeast-2a” may map to a different physical zone for a different user).
Components of a VPC:
- A Virtual Private Cloud: A logically isolated virtual network in the AWS cloud. You define a VPC’s IP address space from ranges you select.
- Subnet: A segment of a VPC’s IP address range where you can place groups of isolated resources (maps to an AZ, 1:1).
- Internet Gateway: The Amazon VPC side of a connection to the public Internet.
- NAT Gateway: A highly available, managed Network Address Translation (NAT) service for your resources in a private subnet to access the Internet.
- Hardware VPN Connection: A hardware-based VPN connection between your Amazon VPC and your datacenter, home network, or co-location facility.
- Virtual Private Gateway: The Amazon VPC side of a VPN connection.
- Customer Gateway: Your side of a VPN connection.
- Router: Routers interconnect subnets and direct traffic between Internet gateways, virtual private gateways, NAT gateways, and subnets.
- Peering Connection: A peering connection enables you to route traffic via private IP addresses between two peered VPCs.
- VPC Endpoints: Enables private connectivity to services hosted in AWS, from within your VPC without using an Internet Gateway, VPN, Network Address Translation (NAT) devices, or firewall proxies.
- Egress-only Internet Gateway: A stateful gateway to provide egress only access for IPv6 traffic from the VPC to the Internet.
Options for securely connecting to a VPC are:
- AWS managed VPN – fast to setup.
- Direct Connect – high bandwidth, low-latency but takes weeks to months to setup.
- VPN CloudHub – used for connecting multiple sites to AWS.
- Software VPN – use 3rd party software.
An Elastic Network Interface (ENI) is a logical networking component that represents a NIC.
ENIs can be attached and detached from EC2 instances, and the configuration of the ENI will be maintained.
Flow Logs capture information about the IP traffic going to and from network interfaces in a VPC.
Flow log data is stored using Amazon CloudWatch Logs.
Flow logs can be created at the following levels:
- VPC.
- Subnet.
- Network interface.
Peering connections can be created with VPCs in different regions (available in most regions now).
Subnets
After creating a VPC, you can add one or more subnets in each Availability Zone.
When you create a subnet, you specify the CIDR block for the subnet, which is a subset of the VPC CIDR block.
Each subnet must reside entirely within one Availability Zone and cannot span zones.
Types of subnet:
- If a subnet’s traffic is routed to an internet gateway, the subnet is known as a public subnet.
- If a subnet doesn’t have a route to the internet gateway, the subnet is known as a private subnet.
- If a subnet doesn’t have a route to the internet gateway, but has its traffic routed to a virtual private gateway for a VPN connection, the subnet is known as a VPN-only subnet.
An Internet Gateway is a horizontally scaled, redundant, and highly available VPC component that allows communication between instances in your VPC and the internet.
Firewalls
Network Access Control Lists (ACLs) provide a firewall/security layer at the subnet level.
Security Groups provide a firewall/security layer at the instance level.
The table below describes some differences between Security Groups and Network ACLs:
| Security Group | Network ACL |
| Operates at the instance (interface) level | Operates at the subnet level |
| Supports allow rules only | Supports allow and deny rules |
| Stateful | Stateless |
| Evaluates all rules | Processes rules in order |
| Applies to an instance only if associated with a group | Automatically applies to all instances in the subnets its associated with |
VPC Wizard
The VPC Wizard can be used to create the following four configurations:VPC with a Single Public Subnet:
- Your instances run in a private, isolated section of the AWS cloud with direct access to the Internet.
- Network access control lists and security groups can be used to provide strict control over inbound and outbound network traffic to your instances.
- Creates a /16 network with a /24 subnet. Public subnet instances use Elastic IPs or Public IPs to access the Internet.
VPC with Public and Private Subnets:
- In addition to containing a public subnet, this configuration adds a private subnet whose instances are not addressable from the Internet.
- Instances in the private subnet can establish outbound connections to the Internet via the public subnet using Network Address Translation (NAT).
- Creates a /16 network with two /24 subnets.
- Public subnet instances use Elastic IPs to access the Internet.
- Private subnet instances access the Internet via Network Address Translation (NAT).
VPC with Public and Private Subnets and Hardware VPN Access:
- This configuration adds an IPsec Virtual Private Network (VPN) connection between your Amazon VPC and your data center – effectively extending your data center to the cloud while also providing direct access to the Internet for public subnet instances in your Amazon VPC.
- Creates a /16 network with two /24 subnets.
- One subnet is directly connected to the Internet while the other subnet is connected to your corporate network via an IPsec VPN tunnel.
VPC with a Private Subnet Only and Hardware VPN Access:
- Your instances run in a private, isolated section of the AWS cloud with a private subnet whose instances are not addressable from the Internet.
- You can connect this private subnet to your corporate data center via an IPsec Virtual Private Network (VPN) tunnel.
- Creates a /16 network with a /24 subnet and provisions an IPsec VPN tunnel between your Amazon VPC and your corporate network.
NAT Instances
NAT instances are managed by you.
Used to enable private subnet instances to access the Internet.
When creating NAT instances always disable the source/destination check on the instance.
NAT instances must be in a single public subnet.
NAT instances need to be assigned to security groups.
NAT Gateways
NAT gateways are managed for you by AWS.
NAT gateways are highly available in each AZ into which they are deployed.
They are preferred by enterprises.
Can scale automatically up to 45Gbps.
No need to patch.
Not associated with any security groups.
The table below describes some differences between NAT instances and NAT gateways:
| NAT Instance | NAT Gateway |
| Managed by you (e.g. software updates) | Managed by AWS |
| Scale up (instance type) manually and use enhanced networking | Elastic scalability up to 45 Gbps |
| No high availability – scripted/auto-scaled HA possible using multiple NATs in multiple subnets | Provides automatic high availability within an AZ and can be placed in multiple AZs |
| Need to assign Security Group | No Security Groups |
| Can use as a bastion host | Cannot access through SSH |
AWS Direct Connect (DX)
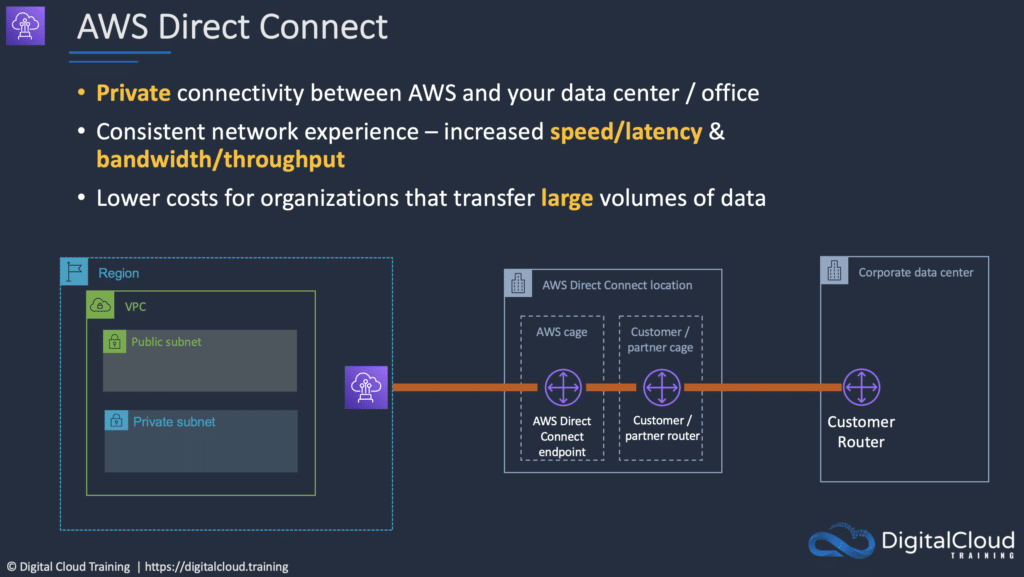
AWS Direct Connect is a network service that provides an alternative to using the Internet to connect a customer’s on-premises sites to AWS.
Data is transmitted through a private network connection between AWS and a customer’s data center or corporate network.
Benefits of Direct Connect:
- Reduce cost when using large volumes of traffic.
- Increase reliability (predictable performance).
- Increase bandwidth (predictable bandwidth).
- Decrease latency.
Each AWS Direct Connect connection can be configured with one or more virtual interfaces (VIFs).
Public VIFs allow access to public services such as S3, EC2, and DynamoDB.
Private VIFs allow access to your VPC.
From Direct Connect you can connect to all AZs within the Region.
You can establish IPSec connections over public VIFs to remote regions.
Direct Connect is charged by port hours and data transfer.
Available in 1Gbps and 10Gbps.
Speeds of 50Mbps, 100Mbps, 200Mbps, 300Mbps, 400Mbps, and 500Mbps can be purchased through AWS Direct Connect Partners.
Each connection consists of a single dedicated connection between ports on the customer router and an Amazon router.
for HA you must have 2 DX connections – can be active/active or active/standby.
Route tables need to be updated to point to a Direct Connect connection.
Elastic Load Balancing
Elastic Load Balancing (ELB) is an Amazon service that automatically distributes incoming application traffic across multiple targets and Availability Zones. It also scales resources to meet traffic demands. ELB distributes traffic to targets, including Amazon EC2 instances, containers, IP addresses and AWS Lambda functions.
This service monitors Amazon EC2 instance health to ensure traffic is routed to properly working instances. Developers can route traffic via a public, internet-facing load balancer or through an internal load balancer for network security purposes.
There are four types of load balancers within ELB that provide automated scaling and high availability:
- Application Load Balancer. Recommended for load balancing HTTP requests and provides routing for application architectures such as microservices and containers. This version of ELB is a OSI Layer 7 load balancer and works at the individual request and application level.
- Network Load Balancer. Best for network/transport protocols load balancing. It is built for load balancing traffic that requires high performance and low latency, including TCP, User Datagram Protocol and Transport Layer Security traffic. Network Load Balancer operates at a Layer 4 connection level.
- Gateway Load Balancer. Better if the user deploys and run third-party virtual appliances, such as firewalls, intrusion detection and prevention systems. It operates at Layer 3, the network layer.
- Classic Load Balancer. Fits applications built within EC2 Classic network. It performs load balancing across Amazon EC2 instances. This is a Layer 4 load balancer that operates at the request and connection level, though it has some Layer 7 functionality. Since is predates the other variants, it should not be used for new services.
Amazon Route 53
Amazon’s scalable DNS web service, Route 53, directs end users to web applications by translating domain names into numbered IP addresses. It is used for three main functions: domain registration, DNS routing and health checking
This DNS service can route users to infrastructure inside and outside of the AWS cloud. Route 53 automatically routes users to the optimal DNS server location in the global network, based on network conditions.
Route 53 supports various routing types, such as geo-DNS, weighted round robin and latency-based routing. The Amazon Route 53 has a traffic flow feature that provide a visual editor that helps users create and maintain records in large and complex configurations as well as define policies for how end-user traffic is routed to applications.
Amazon CloudFront
Amazon CloudFront is AWS’ native content delivery network (CDN) service. Organizations use CloudFront to quickly distribute both static and dynamic content. The CDN routes each request through the AWS network and to the nearest edge location to provide the fastest delivery path to end users. CloudFront also reduces the number of networks a user’s request passes through in the content delivery process.
It is commonly used to accelerate static website content delivery as well as enable video on demand and live streaming video.
AWS Direct Connect
AWS Direct Connect provides a private connection between a customer’s on-premises data center and the cloud without using the public internet. This Amazon networking service uses an Ethernet cable to connect an organization’s internal workloads to one of AWS’ Direct Connect locations. Its offers connection speeds from 50 Mbps to 100 Gbps.
This connection creates multiple virtual interfaces to Amazon’s publicly accessible cloud services or to private resources hosted on AWS. Users can access private and public resources with the same connection while maintaining network separation between the two environments. AWS Direct Connect is particularly useful for organizations with strict governance and compliance rules that require private connectivity.
AWS cloud users can choose between two types of connections with this service:
- Dedicated. The dedicated connection uses an Ethernet cable to create a connection with an individual customer. AWS cloud users request a dedicated connection through the AWS Direct Connect console, the command line interface or the API.
- Hosted. The hosted connection requires an AWS Direct Connect Partner to provision the physical Ethernet connection on behalf of a customer. For the hosted connection, IT teams must choose a partner in the AWS Direct Connect Delivery Partners Program.
AWS Virtual Private Network
AWS VPN enables enterprises to connect their on-premises network to cloud users. The platform provides two VPN options: AWS Site-to-Site VPN and AWS Client VPN.
- AWS Site-to-Site VPN. Creates a secure, encrypted connection between an on-premises facility and an Amazon VPC environment as well as AWS Transit Gateway. There is an Accelerated Site-to-Site VPN option, which works AWS Global Accelerator, that improves VPN connection performance.
- AWS Client VPN. Enables employees to securely access a company’s resources — both on AWS and within on-premises networks — remotely. The Client VPN is a fully managed, elastic VPN service that covers provisioning and capacity as well as scales automatically.
AWS Transit Gateway
AWS Transit Gateway connects Amazon VPCs and on-premises networks across multiple accounts through a central hub. Every new connection is made once as the tool acts as a highly scalable cloud router. It is useful for organizations with hybrid cloud architectures. It supports dynamic and static Layer 3 routing between Amazon VPCs and VPN.
AWS users can centrally monitor their network with the Transit Gateway Network Manager, which provides events and metrics to monitor the entire network — both cloud and on premises. AWS Transit Gateway Connect enables native integration of SD-WAN appliances into AWS.
This networking service also offers an inter-region peering feature to connect networks and share resources in different AWS regions as well as multicast features.
AWS Global Accelerator
This networking offering improves application availability and performance for globally distributed end users. AWS Global accelerator provides a static public IP address that works as a single fixed entry point and is associated to a regional endpoint. The static IP address accepts incoming traffic onto AWS’ global network from the closest edge location. Global Accelerator then directs network traffic to an endpoint on the most efficient path based on geographical location, application health and routing policies set by the developer. In the event of any issues, Global Accelerator automatically redirects traffic to healthy endpoints.
AWS PrivateLink
PrivateLink provides a secure, private connection between Amazon VPCs and other resources that run on AWS or on-premises applications. It establishes a private IP address with an elastic network interface in the subnet and provides a connection that protects data from public internet exposure.
PrivateLink integrates with AWS Direct Connect to provide a secure interface for on-premises applications. By blocking public exposure, PrivateLink helps mitigate certain network security threats such as brute force and distributed denial-of-service attacks.
AWS App Mesh
AWS App Mesh provides application-level networking and enables services to communicate across several types of compute infrastructure. App Mesh uses Envoy, an open source service mesh proxy that runs alongside an enterprise’s microservice containers.
By standardizing services communication, AWS App Mesh streamlines operations, configures traffic flows, identifies application issues and enhances network security. Users can monitor, control and debug communications between services. It also determines where errors are occurring and will reroute traffic based off these failures. This takes the pressure off organizations to manually build monitoring and control code every time a failure occurs.
AWS Cloud Map
AWS Cloud Map, a cloud resource discovery service, creates custom names for application resources and automatically updates the resources’ locations. The service maintains the updated location of resources that are dynamically changing through endpoints that are statically coded into your application. In turn, this increases application availability. Additionally, development teams will no longer have to store, track and update resource names and location information as AWS Cloud Map provides a single registry for application services.
Reference
- AWS Networking and Content Delivery https://aws.amazon.com/products/networking/